Attack Surface Discovery
The video opens the page from the menu, then walks through the discovered assets, the action bar, the search bar, the confirmed assets and the graph map.
What is Attack Surface Discovery / Management?
Attack surface discovery enables continuous monitoring of an organization's infrastructure to detect missing and rogue assets. Coupled with vulnerability scanning, it ensures complete coverage of an organization's exposure.
Attack surface discovery helps with finding blind spots, common examples are forgotten or missing acquisition infrastructure, unaccounted for dev and production machines or lost assets during internal restructuring and staff change.
Ostorlab's Attack Surface Discovery finds internet-facing assets, be it domains and subdomains, IPv4 and IPv6 addresses,
and Mobile Applications on both Google Play Store and iOS App Store.
Ostorlab's Attack Surface Discovery provides:
- Graph-based asset correlation that goes beyond subdomain enumeration. Other asset discovery techniques include registry correlation, shallow crawling, shared analytics, reverse lookups, etc.
- Asset Management using a hierarchical ownership model grouped into 4 categories,
Internal,Acquisition,3rd Party Service, andRejected. - Continuous Asset Scanning using either intelligent asset change detection, like a website cache invalidation header, Mobile Application release, or using simple time scheduling CRON rules.
- A graph of your attack surface to identify asset connections.
- Search and filters to zoom in on selected portions of the attack surface or the organization hierarchy.
Finding your Attack Surface
Discovering an attack surface starts by seeding in a list of known assets. This includes IP addresses, domain names, or Mobile Applications. Individual assets can be added or a bulk upload using a CSV file is also possible.
Open the page from the menu: Attack Surface, then Discovery. The page has three views, selected at the top of the page:
- Confirmed Assets: the assets you own.
- Discovered Assets: the assets Ostorlab found by expanding from the ones you own, each with a confidence score and a potential owner.
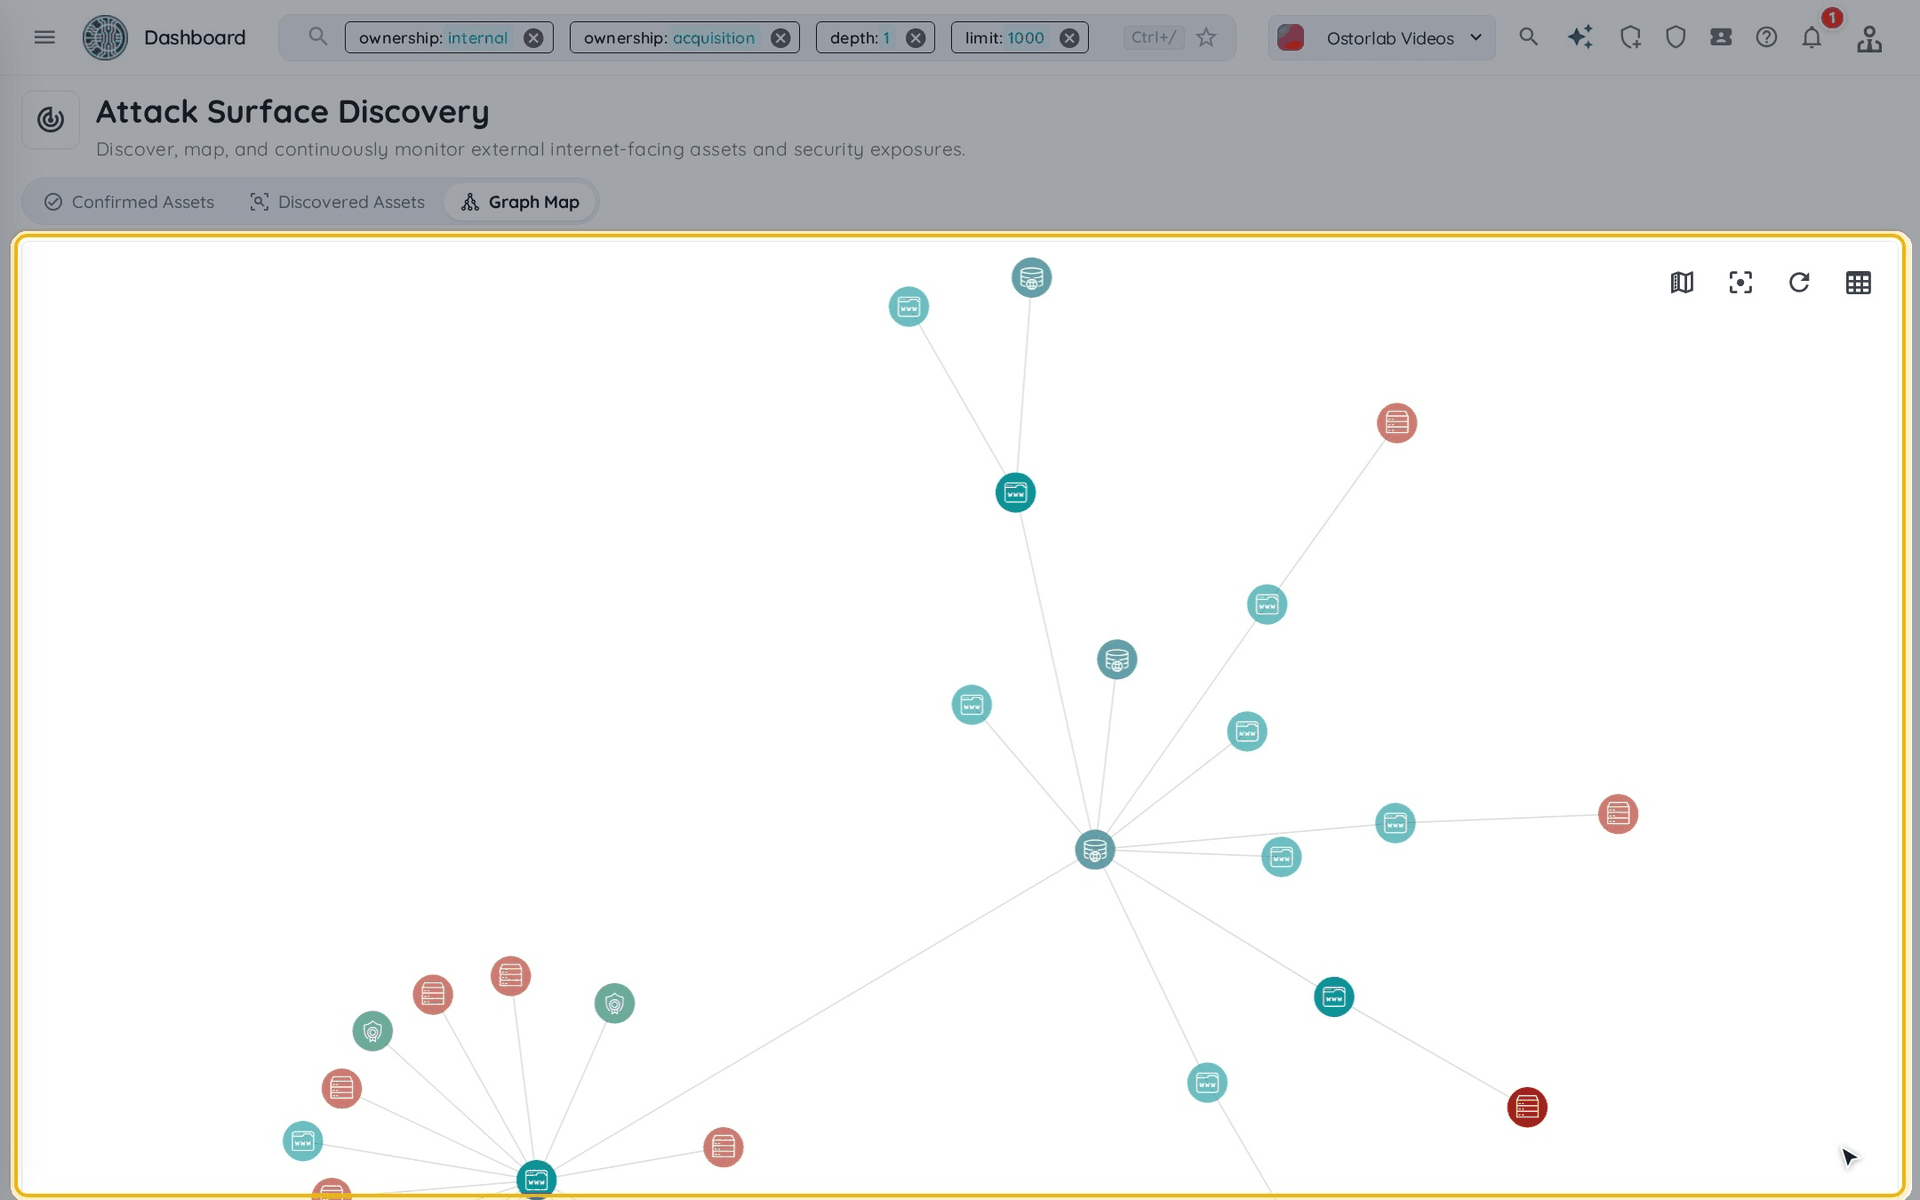
- Graph Map: a graph of all assets and how they connect.
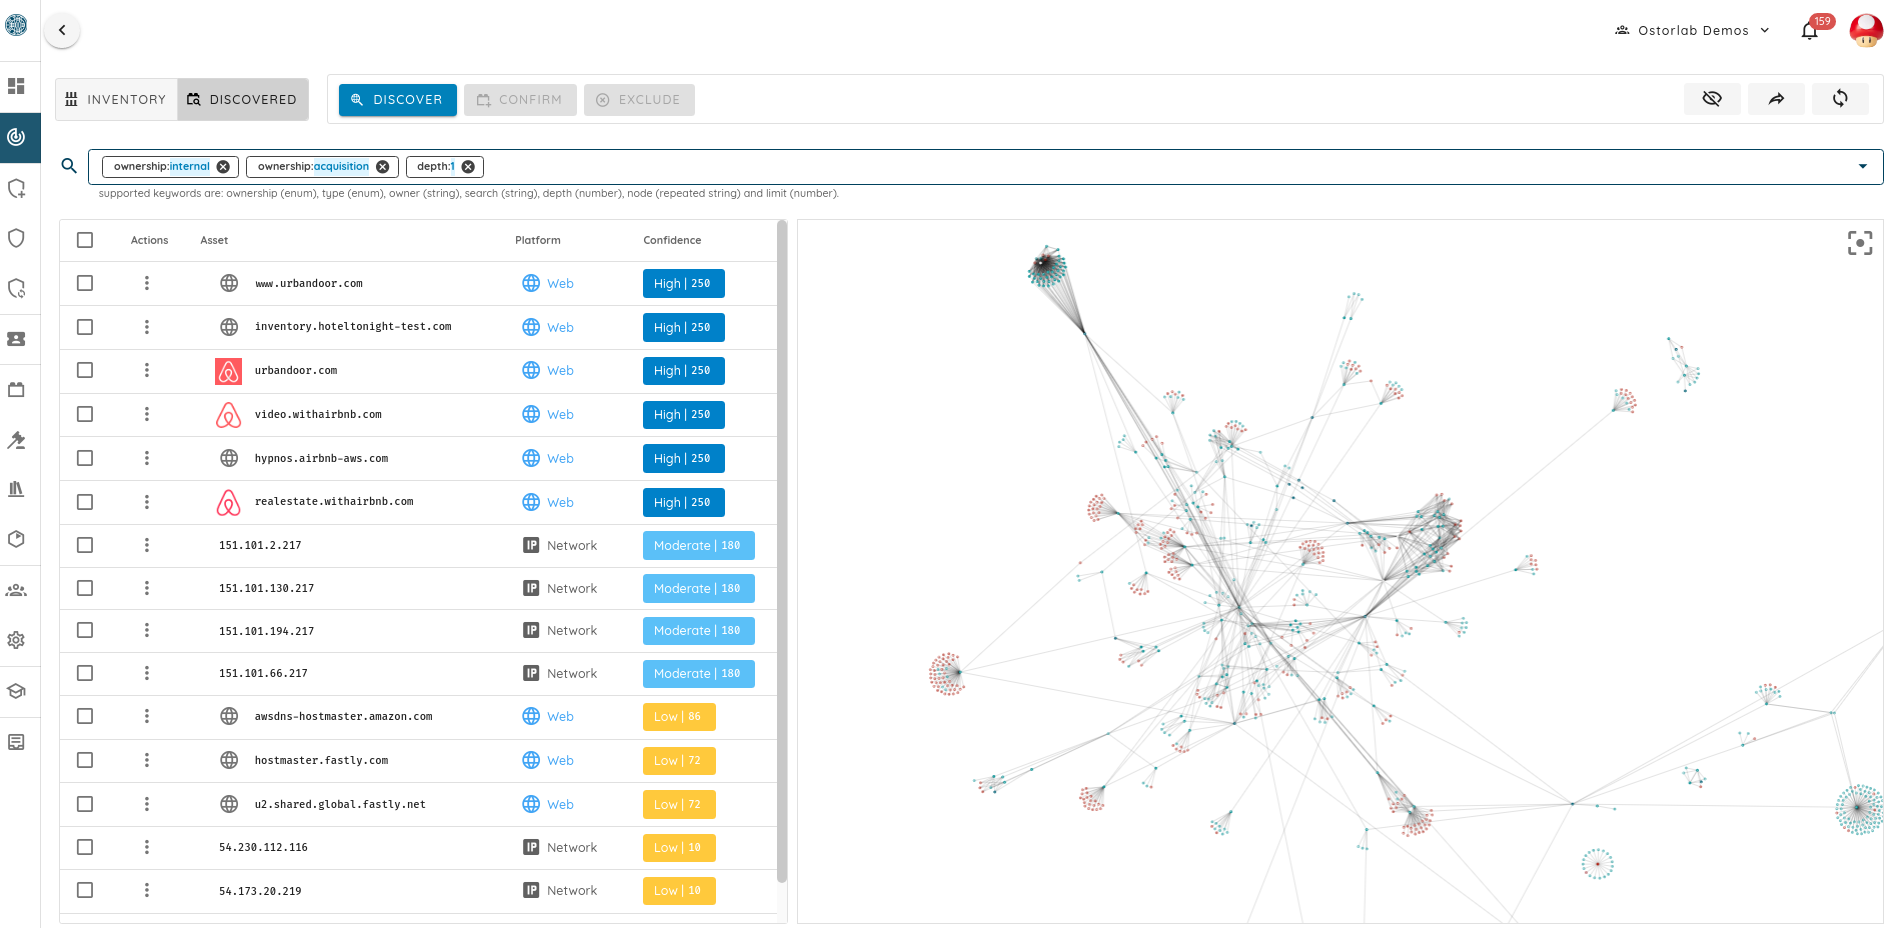
Discovered assets
Each table view has an action bar. The table below lists the Discovered Assets action bar. In this view, first select the assets you want to act on: Confirm, Edit Owner and Exclude apply only to the current selection.
| Action | What it does | Shortcut |
|---|---|---|
| Trigger Discovery | Looks for new assets, starting from the ones you own | t |
| Confirm | Adds the selected assets to your confirmed assets | c |
| Edit Owner | Changes the owner of the selected assets | o |
| Exclude | Marks the selected assets as not yours | x |
| Export | Exports the assets in the view | Shift+e |
| Automate | Sets up automation for the assets in the view | m |
| Refresh | Reloads the view | r |
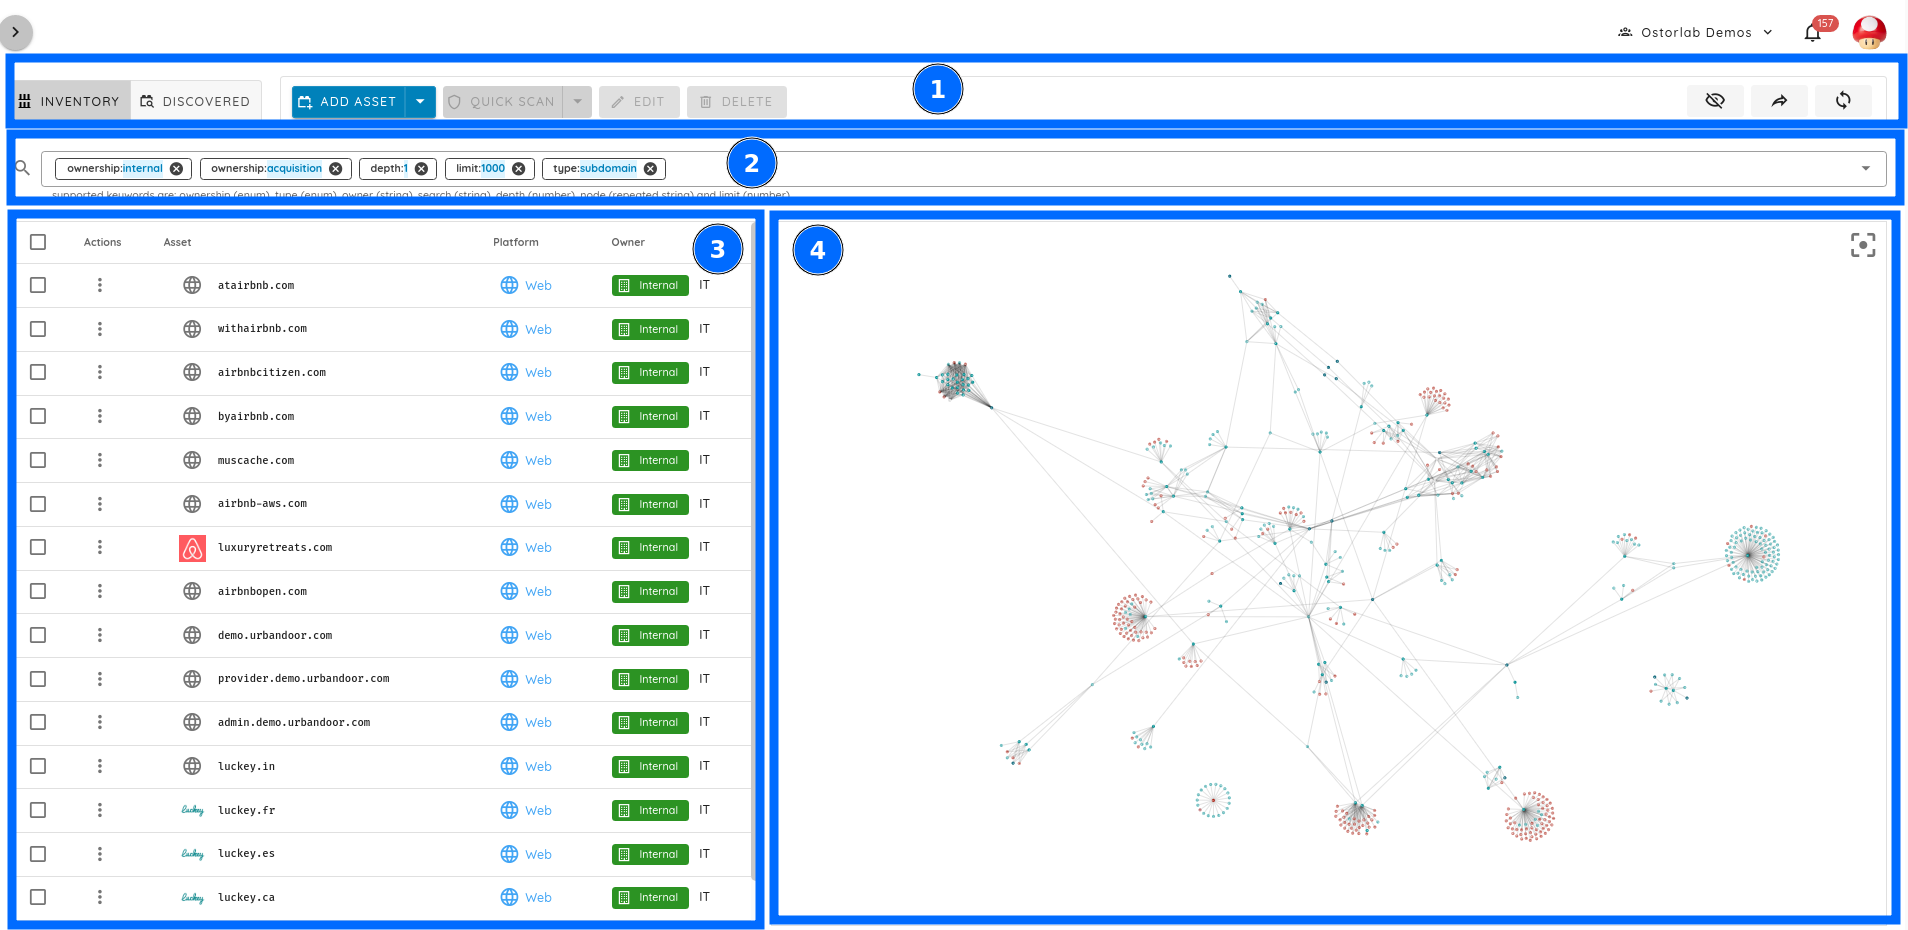
Search and filter
The search bar at the top of the page filters every view: the tables and the graph. It starts with the Internal and
Acquisition owners selected.
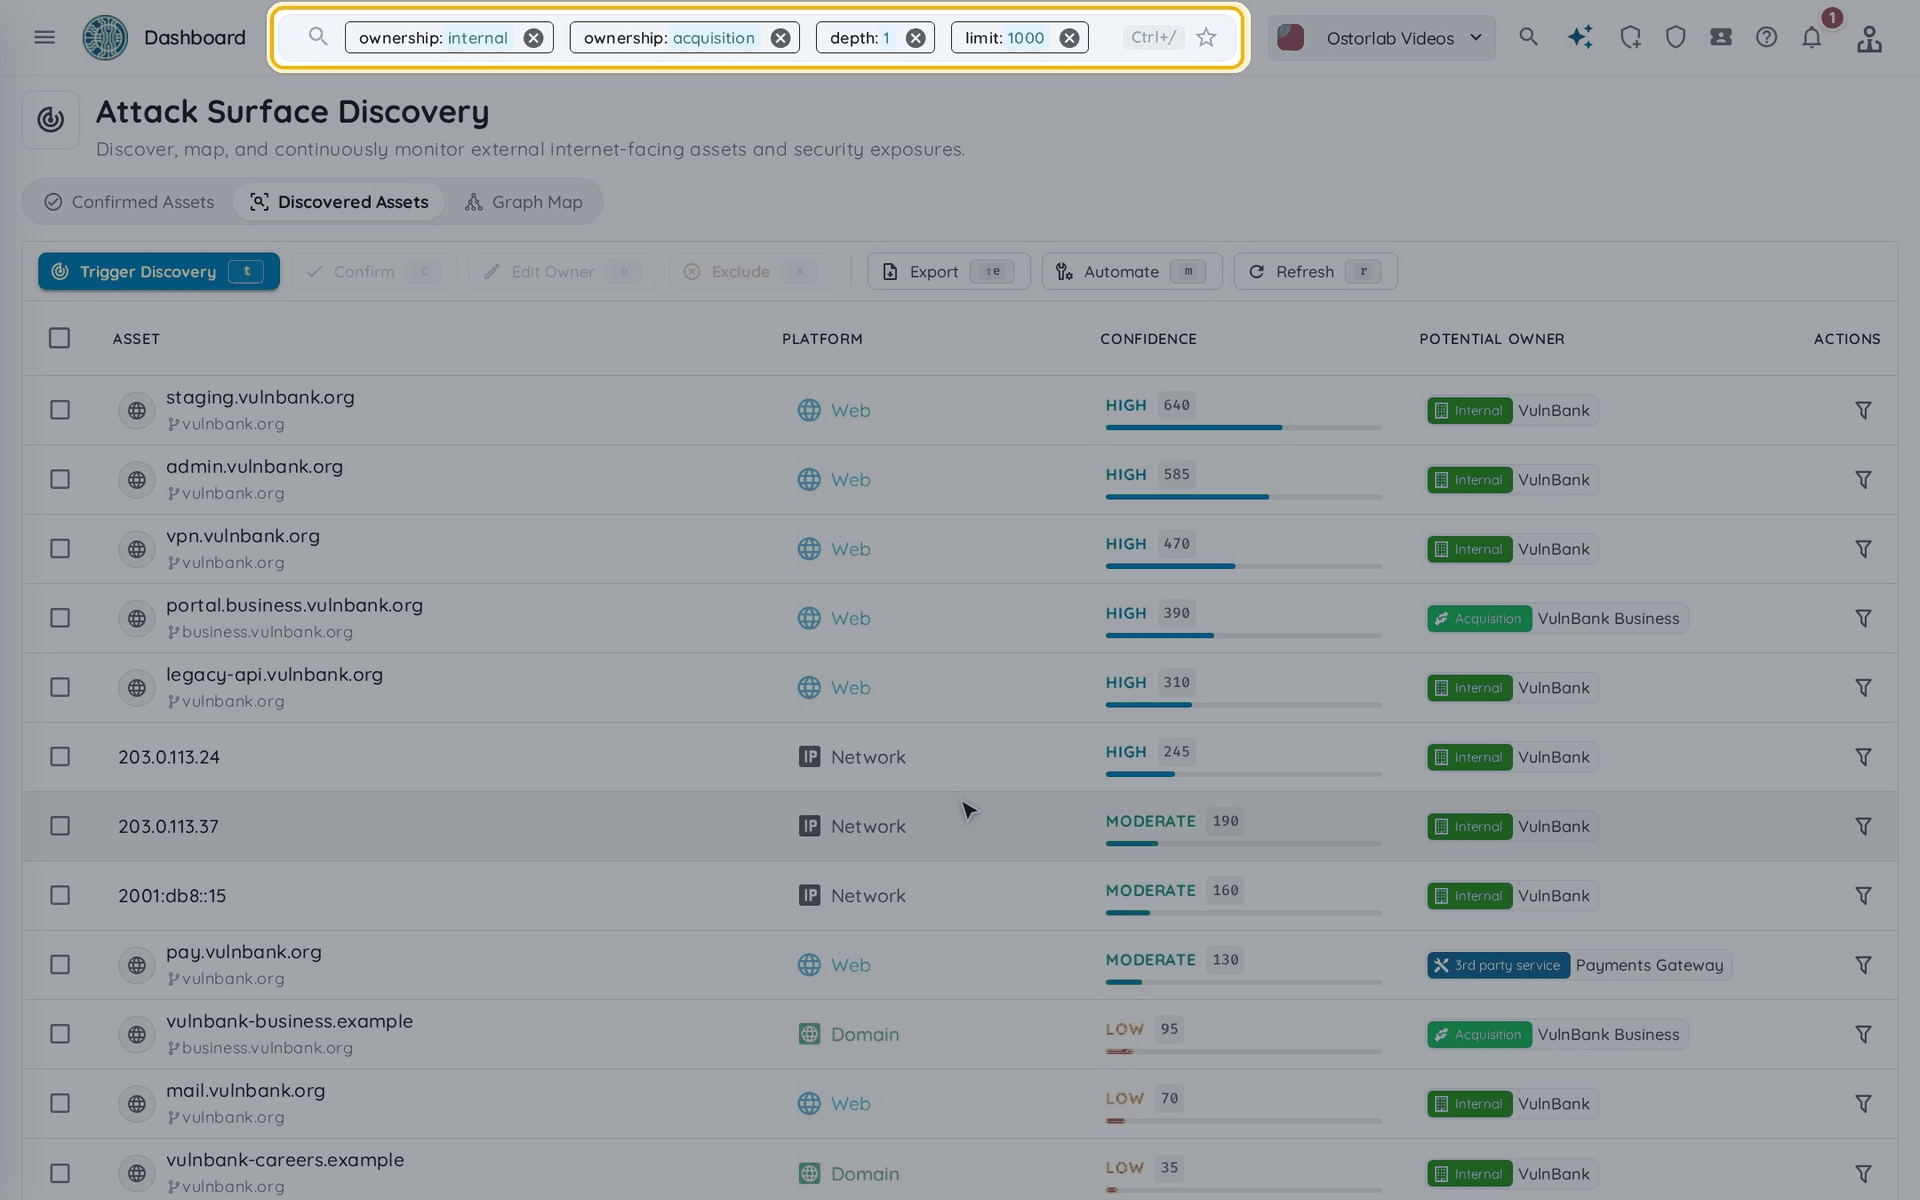
Confirmed assets
Confirmed Assets lists the assets you own, with their platform and owner. Use its action bar to add, edit and delete assets, and to start scans or monitoring on the ones you select (Scan & Monitor).
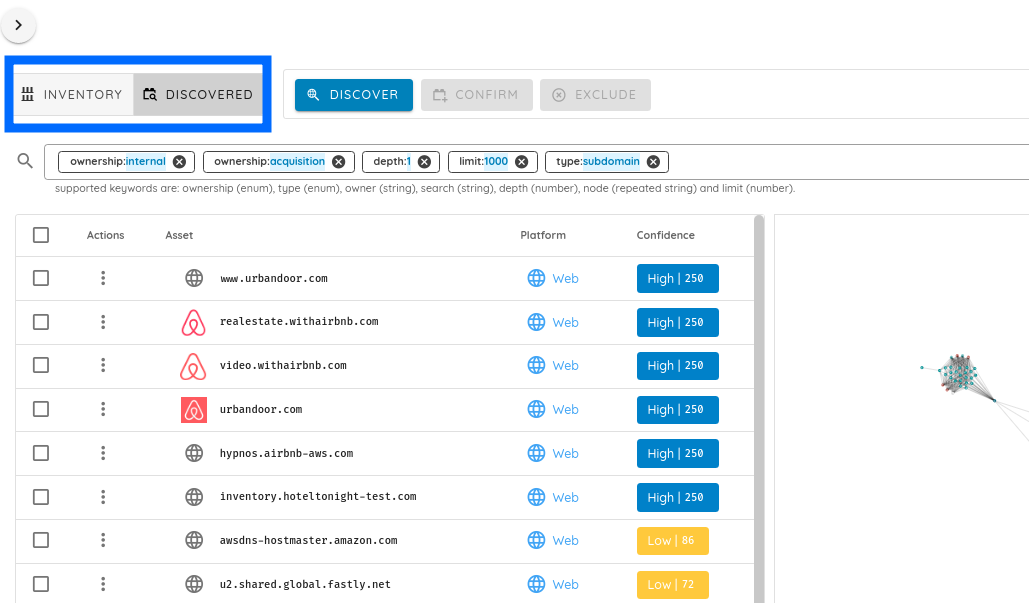
Graph map
Graph Map shows the domains, subdomains, IP addresses and certificates found, and how they connect. Click
Zoom to Fit (or press f) to see the whole map.
Next steps
To map your attack surface, add your first assets or import a list from a CSV file, then click Trigger Discovery.