Detection
Ostorlab's static analysis runs configuration checks, 3rd party dependency fingerprinting, hardcoded secret detection and taint analysis, and its dynamic analysis runs the app in an instrumented sandbox to track its interactions with the network, filesystem, keychain and APIs. Ostorlab targets system backends collected during dynamic analysis to identify server-side vulnerabilities.
Static Analysis
Ostorlab’s Static analysis uses multiple techniques to identify vulnerabilities:
Configuration Checks
Configuration checks for insecure settings. These settings include Android and iOS native parameters, like
AndroidManifest.xml debug and backup mode, Cordova Framework parameters, like Cordova whitelist or debug mode.
For a full list of checks, see knowledge database section.
3rd Party Dependencies
The 3rd party dependency check fingerprints the application's dependencies across supported frameworks, like native Android, iOS CocoaPods, Cordova plugins, and Xamarin DLLs.
The 3rd Party dependencies also fingerprint statically compiled dependencies and identify a large set of libraries like OpenSSL, Zlib, Libjpeg, Libpng, Xerces ....
The fingerprints are matched against the known vulnerabilities database. The database contains both publicly reported vulnerabilities, and a list of non-reported vulnerabilities identified by analyzing public source code repositories.
Hardcoded Secrets
The static engine searches for hardcoded secrets, like API Keys that shouldn't be deployed in a mobile application, as well as passwords, tokens and encryption keys and IV.
Identified secrets are tested for validation and impact by checking permissions, roles and accessible services.
Taint Analysis
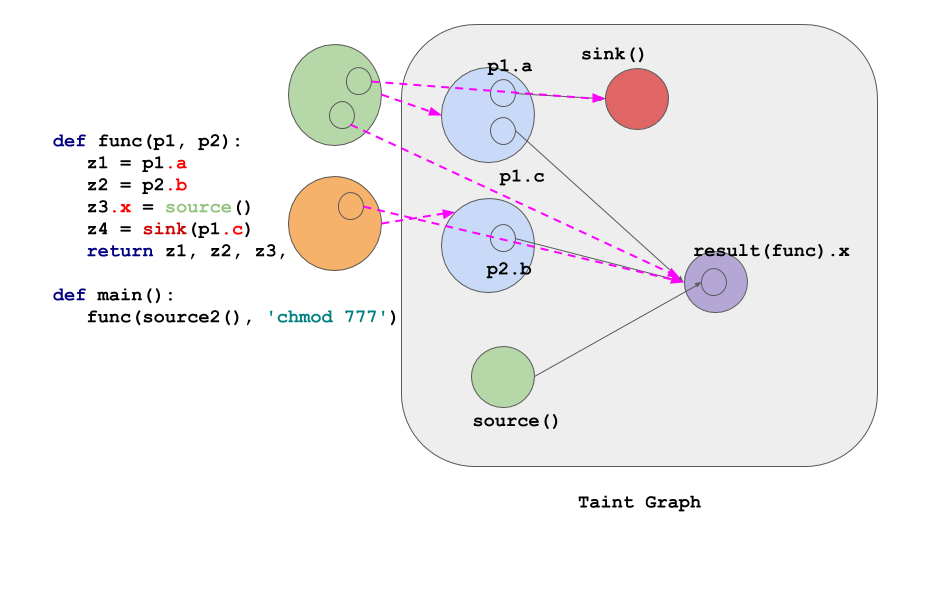
Ostorlab’s core static technology is its taint engine, which tracks how taints propagate over several possible execution paths while taking into account object-oriented and typing information. Dozens of rules then use that taint info to identify vulnerabilities, like SQL injection, command injection, or the use of hardcoded keys.
Dynamic Analysis
Ostorlab runs mobile applications in an instrumented sandbox to track interactions with the external environment, like network, filesystem, keychain, API, etc.
The instrumentation engine tracks calls to standard APIs to identify unsafe arguments, like weak encryption schemes, unsafe RPC calls, code loading from untrusted paths or command execution with user input.
Ostorlab instrumentation collects the app's network traffic, including encrypted traffic. TLS pinning can still prevent traffic interception in some apps; see Mobile Scan Prerequisites. The collected backend is then reused to perform backend analysis.
The dynamic instrumentation uses both system instrumentation techniques, like Fanotify for file system access and a custom non-pervasive runtime instrumentation engine, using JDWP and debug APIs for Android and iOS.
Compared to pervasive methods, like inline hooking that requires custom memory manipulation, this approach collects runtime information through JDWP and the debug APIs, including for iOS applications built using Objective C and Swift, and needs less maintenance when a new system release modifies the underlying system runtime.
Backend
Ostorlab targets collected backends during dynamic analysis to identify server-side vulnerabilities. The analysis is both passive, like detecting the presence of insecure HTTP headers as well as active, like detecting SQL injection or XXE.
Ostorlab uses an advanced Cross-Site Scripting (XSS) scanner agent with dynamic Chrome-based testing and powerful polyglot payloads. The scanner also uses methods like integration of JavaScript Proxy object instrumentation into the preliminary profiling of web applications to streamline the detection of nuanced XSS vectors.
Ostorlab's active testing uses a probabilistic approach to identify vulnerabilities. This approach has the advantage of avoiding the need to send a full payload which could be blocked, limited to a particular OS, may impact the backend stability or trigger intrusion detection systems or application firewalls.
In addition, Ostorlab automates the detection of critical, high-severity, and actively exploitable vulnerabilities sourced from reputable platforms like CISA's KEV, Google’s Tsunami, and the innovative Ostorlab’s Asteroid Project.
Ostorlab backend analysis engine supports a large set of serialization schemes and supports nested serialization injection.
Probabilistic testing coupled with safe rate-limiting protects backend systems from unexpected failures and unwanted denial of service.