Attack Surface Monitoring
A monitoring rule scans your assets again, either when they change or on a schedule. Create one from the assets you own, in Attack Surface, Discovery.
1. Select the assets
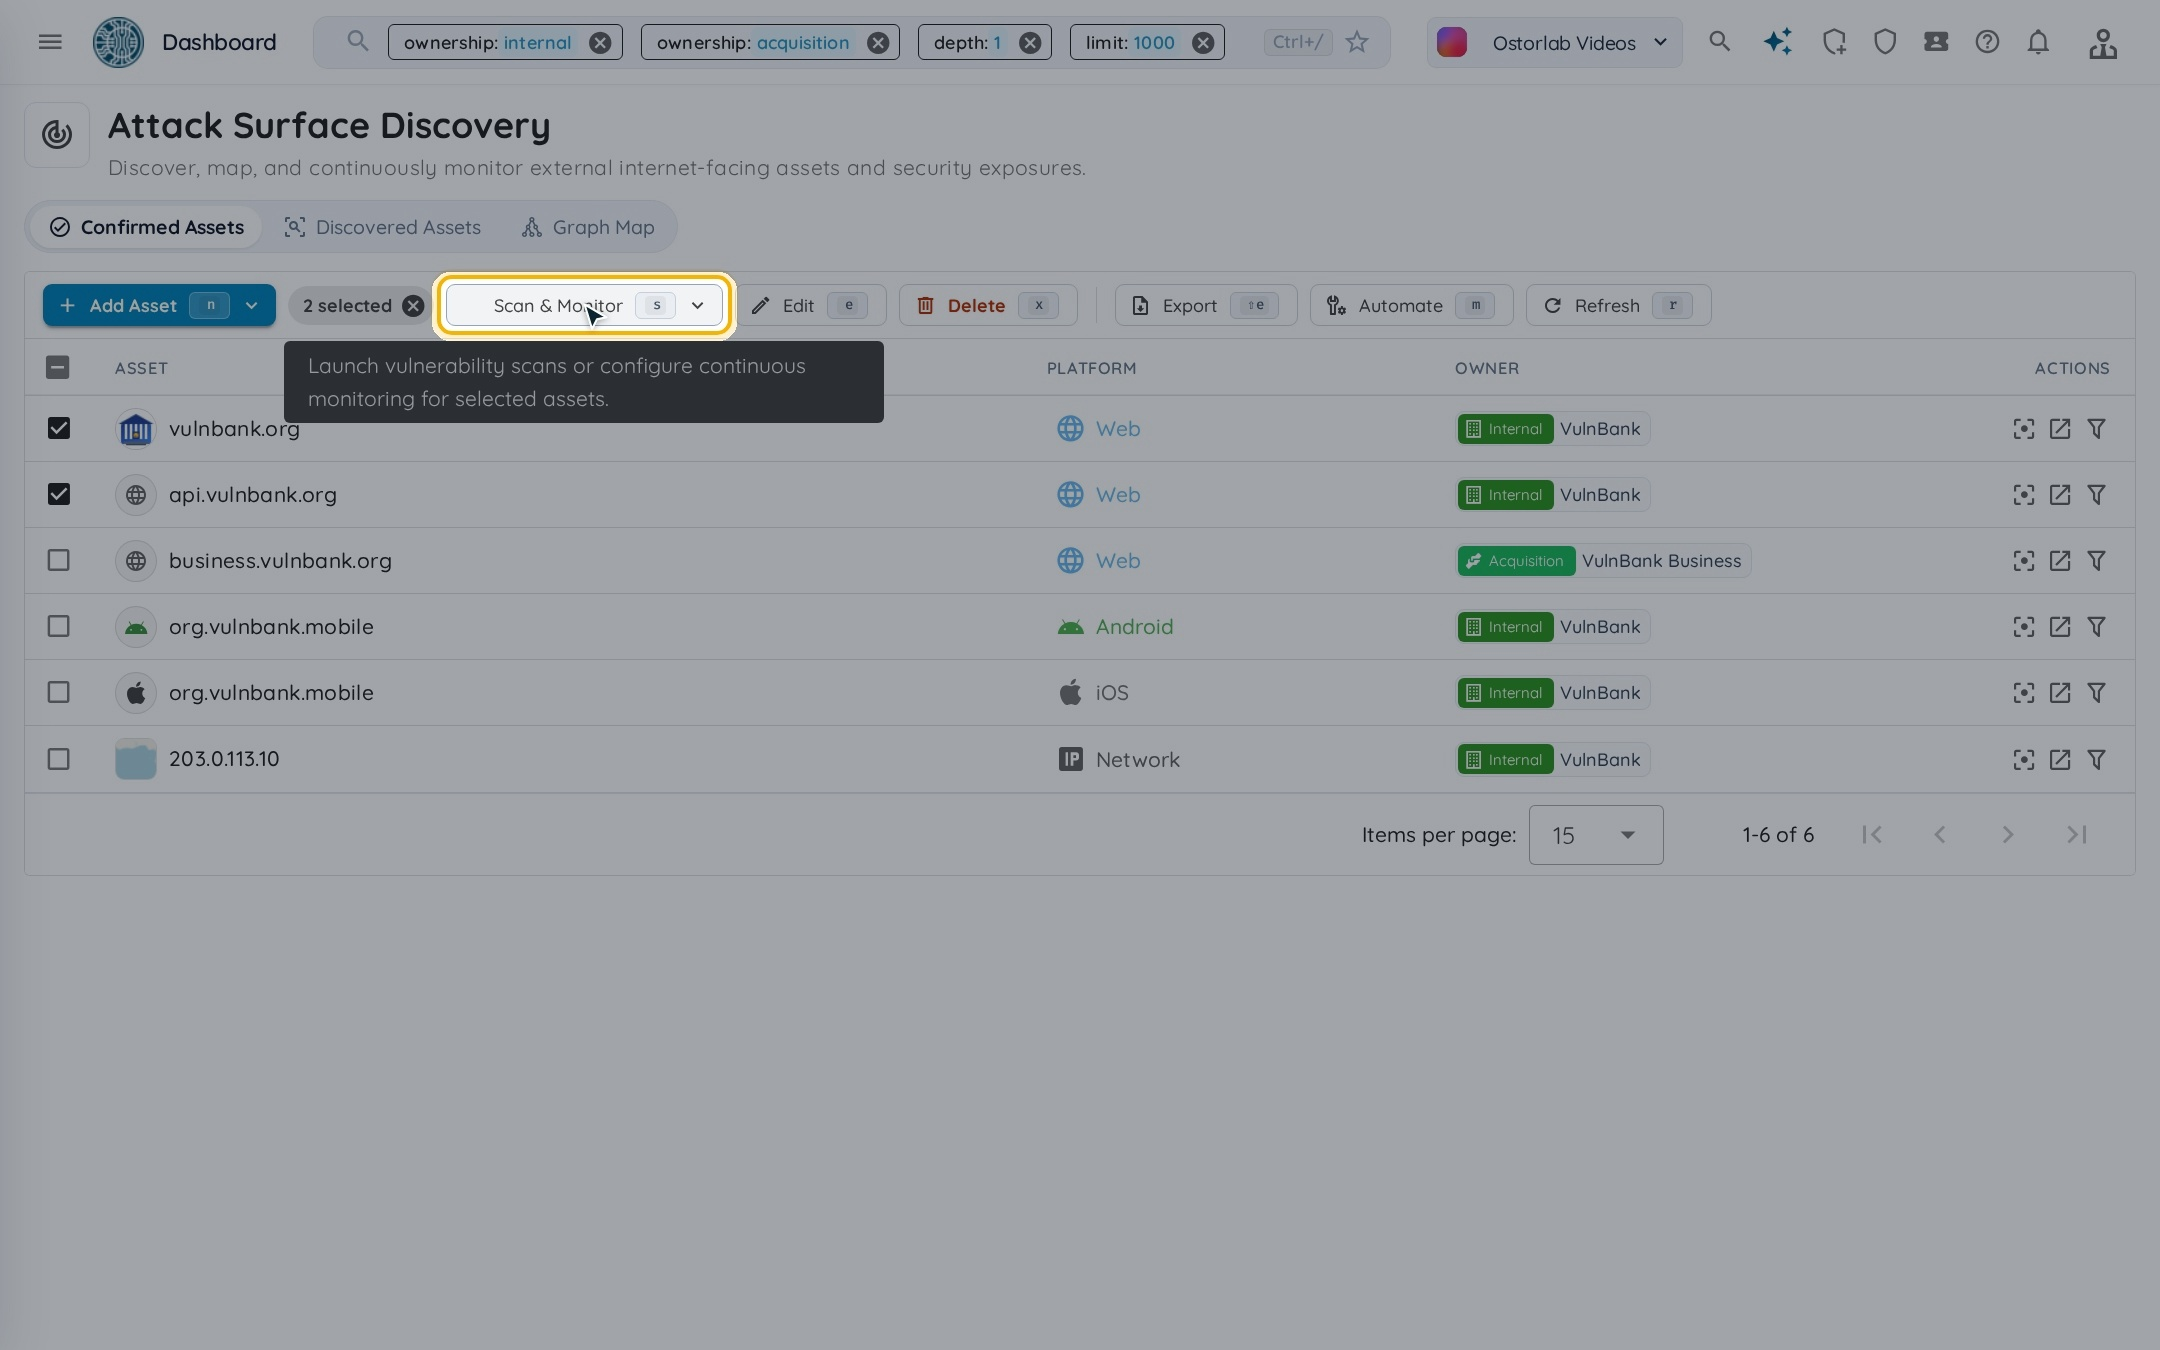
In the menu, open Attack Surface, then Discovery. In Confirmed Assets, select the assets to monitor, then open Scan & Monitor.
Only assets of the same type can be grouped into a single monitoring rule.
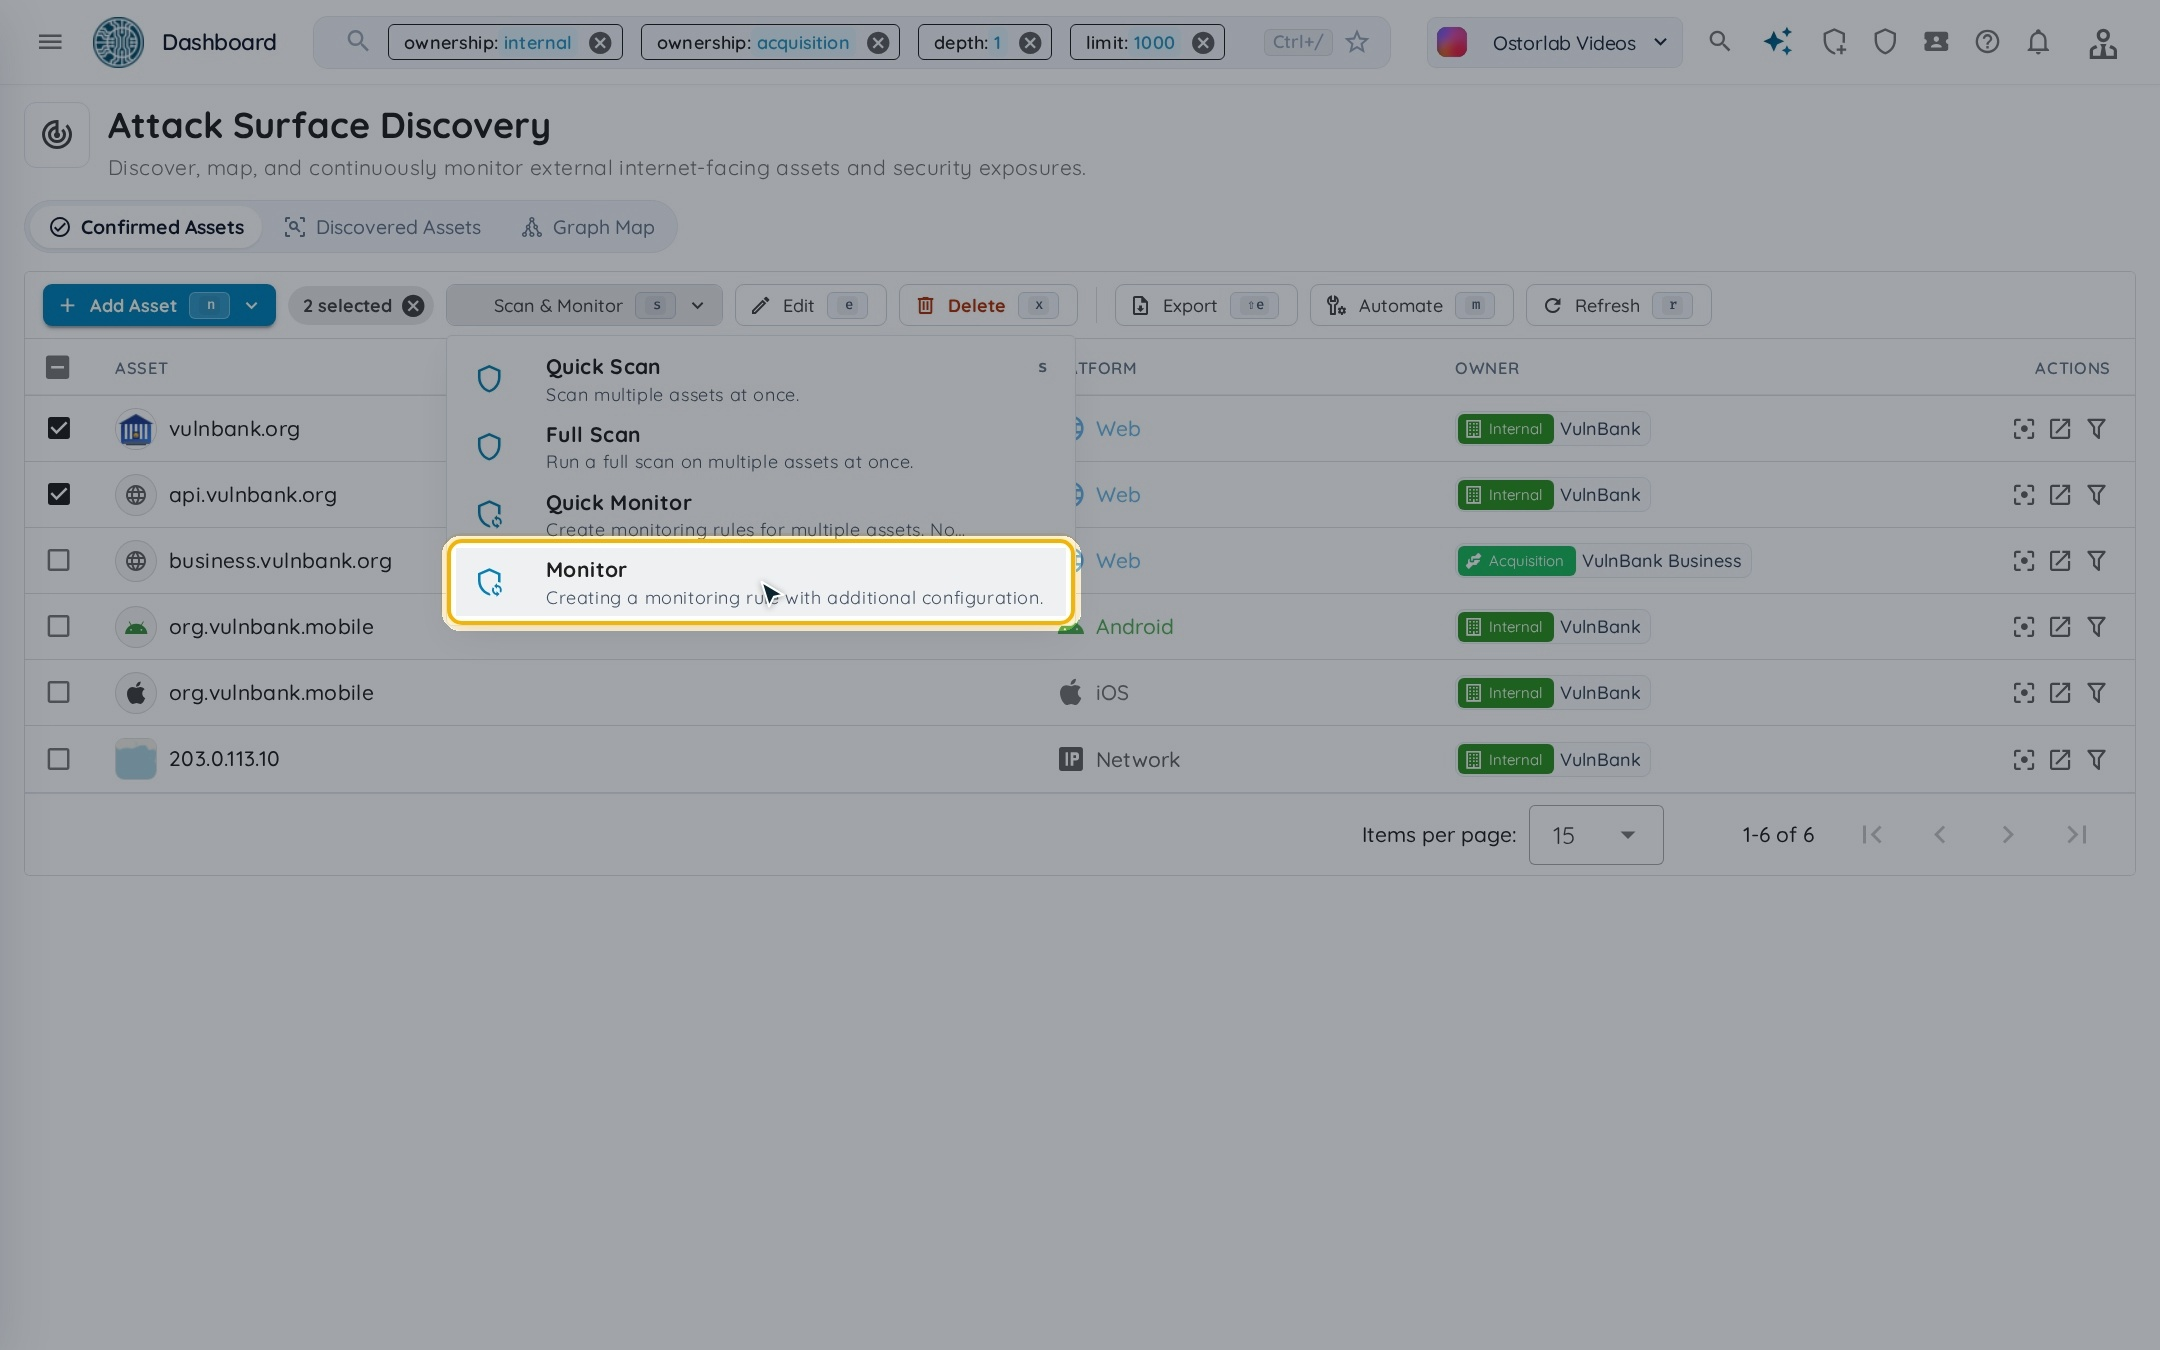
2. Click Monitor
Quick Monitor creates monitoring rules for the selected assets with the default settings. Monitor opens the New Monitoring Rule form, where you configure the rule.
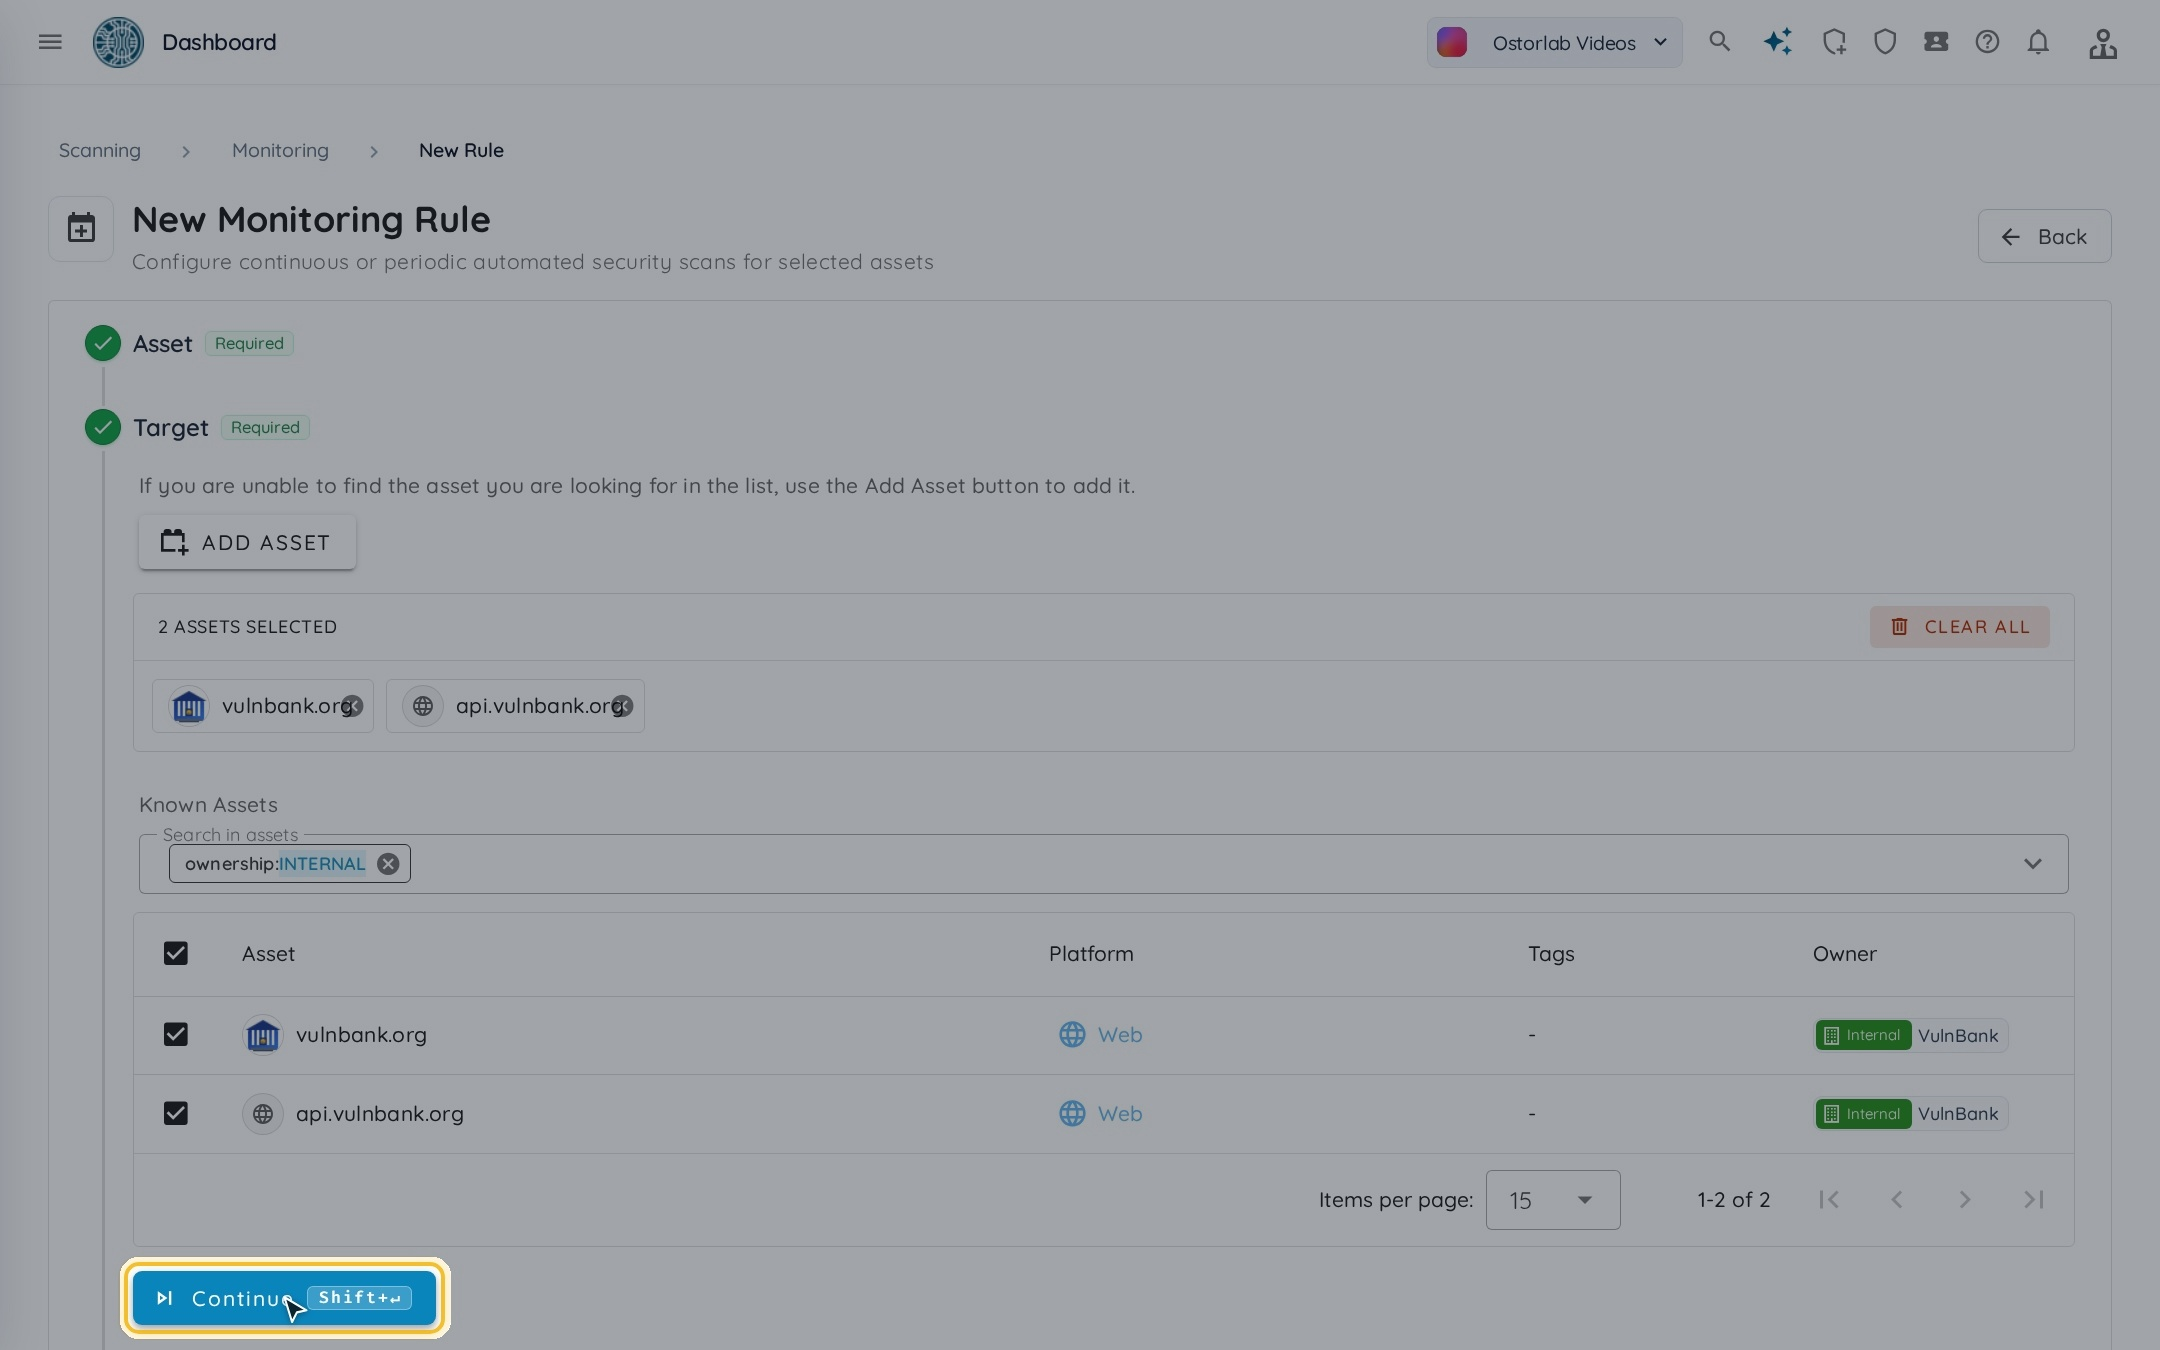
3. Choose the asset type and the targets
In Asset, choose the asset type, for example Web App.
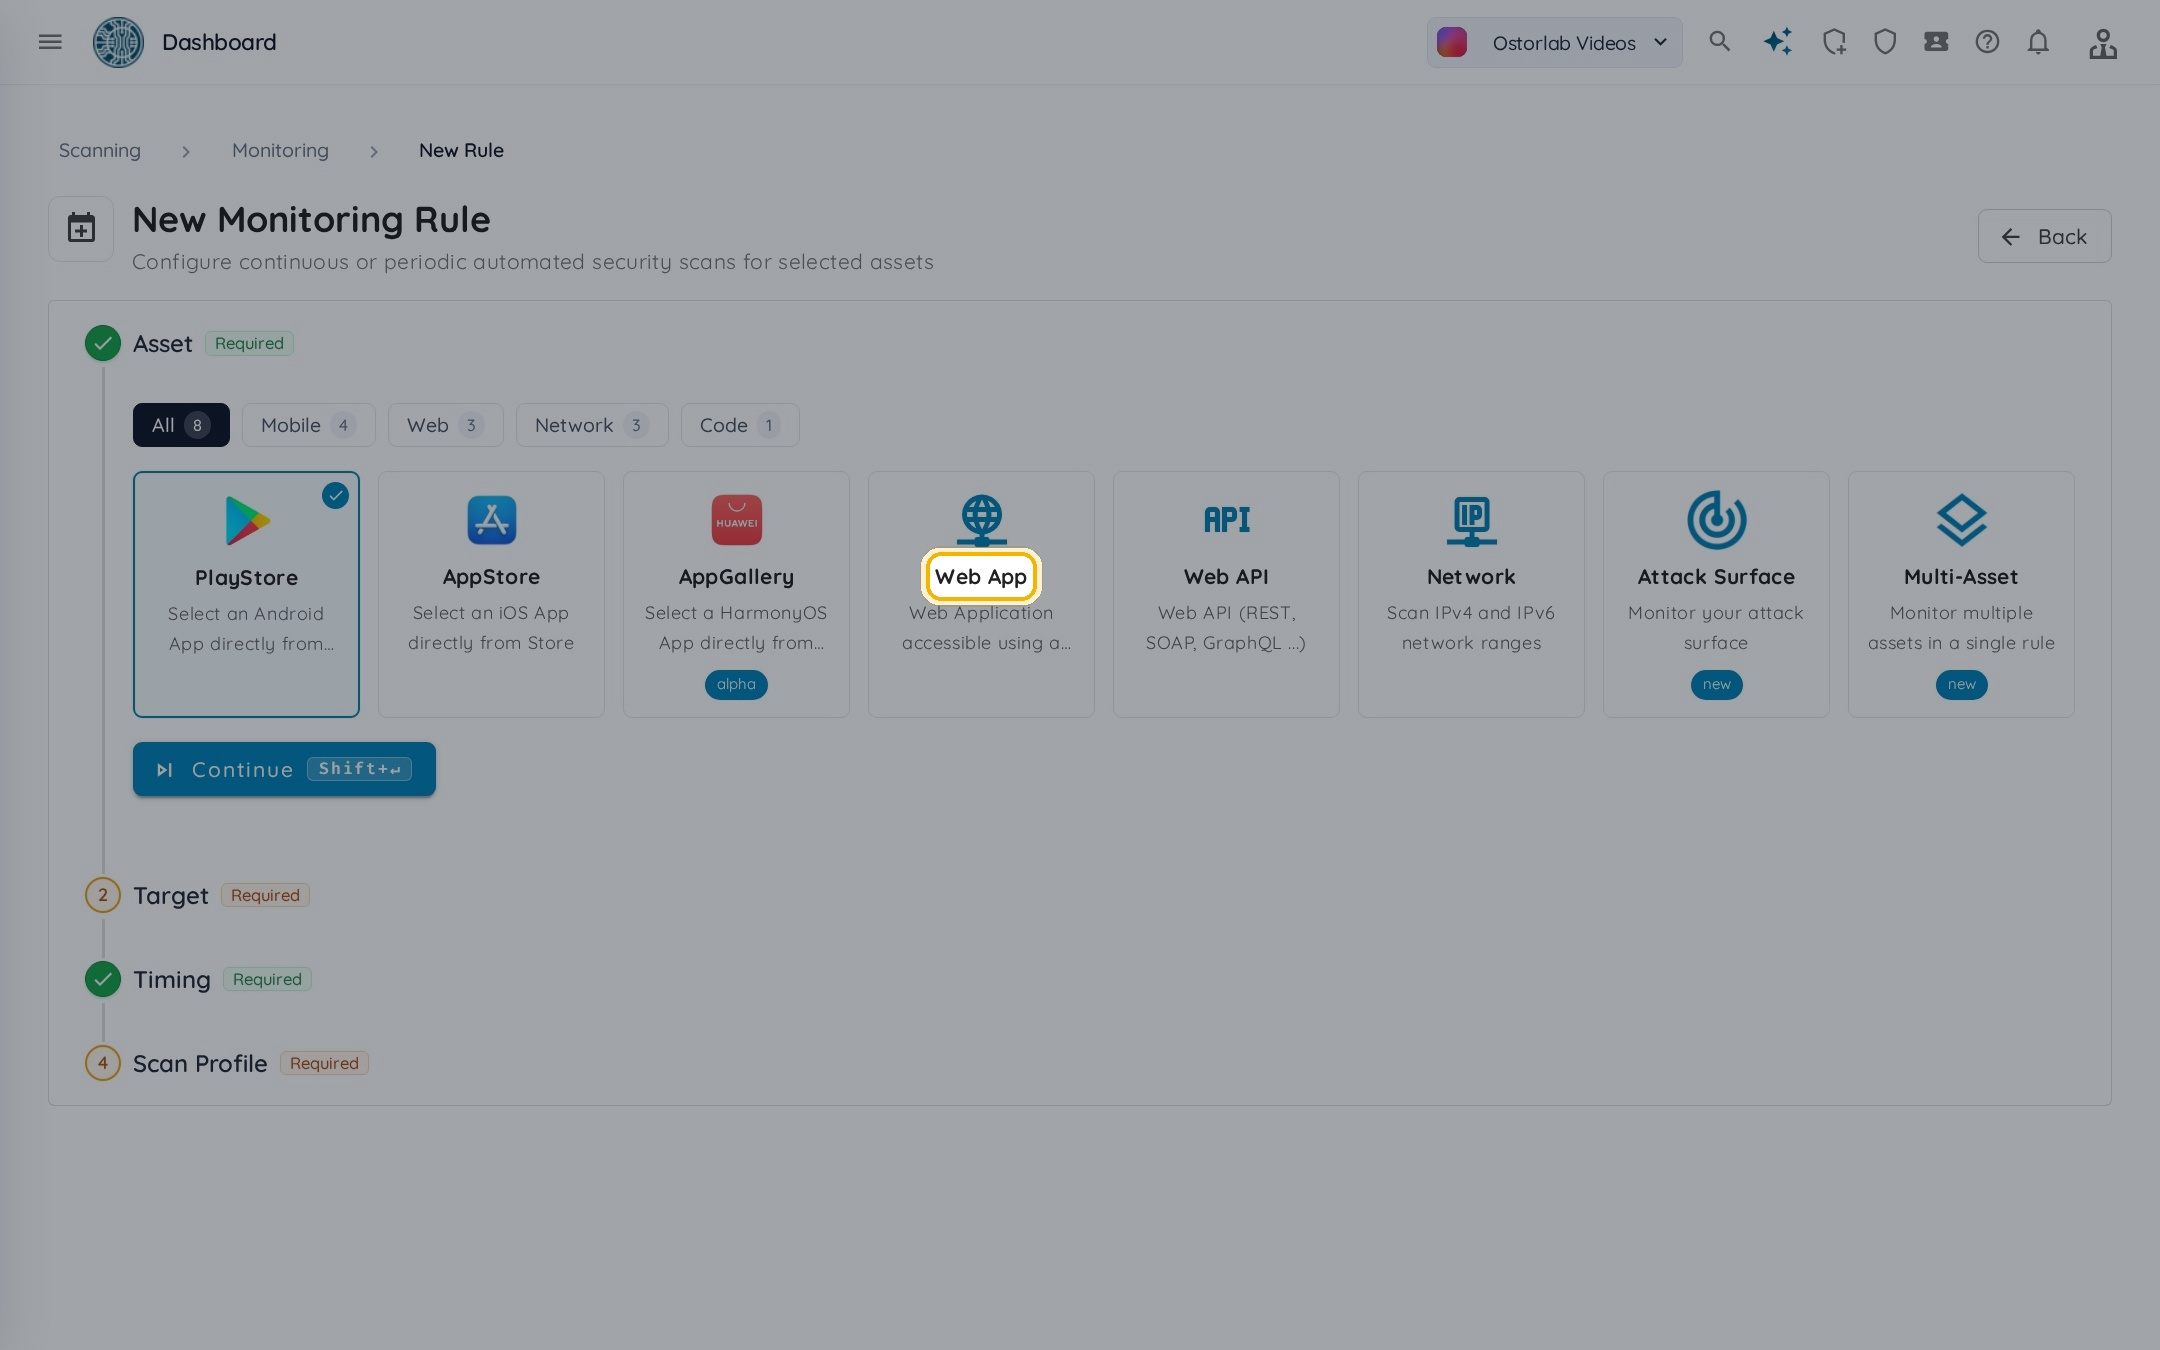
In Target, select the assets the rule scans, then click Continue. To monitor an asset that is not in the list, click Add Asset.
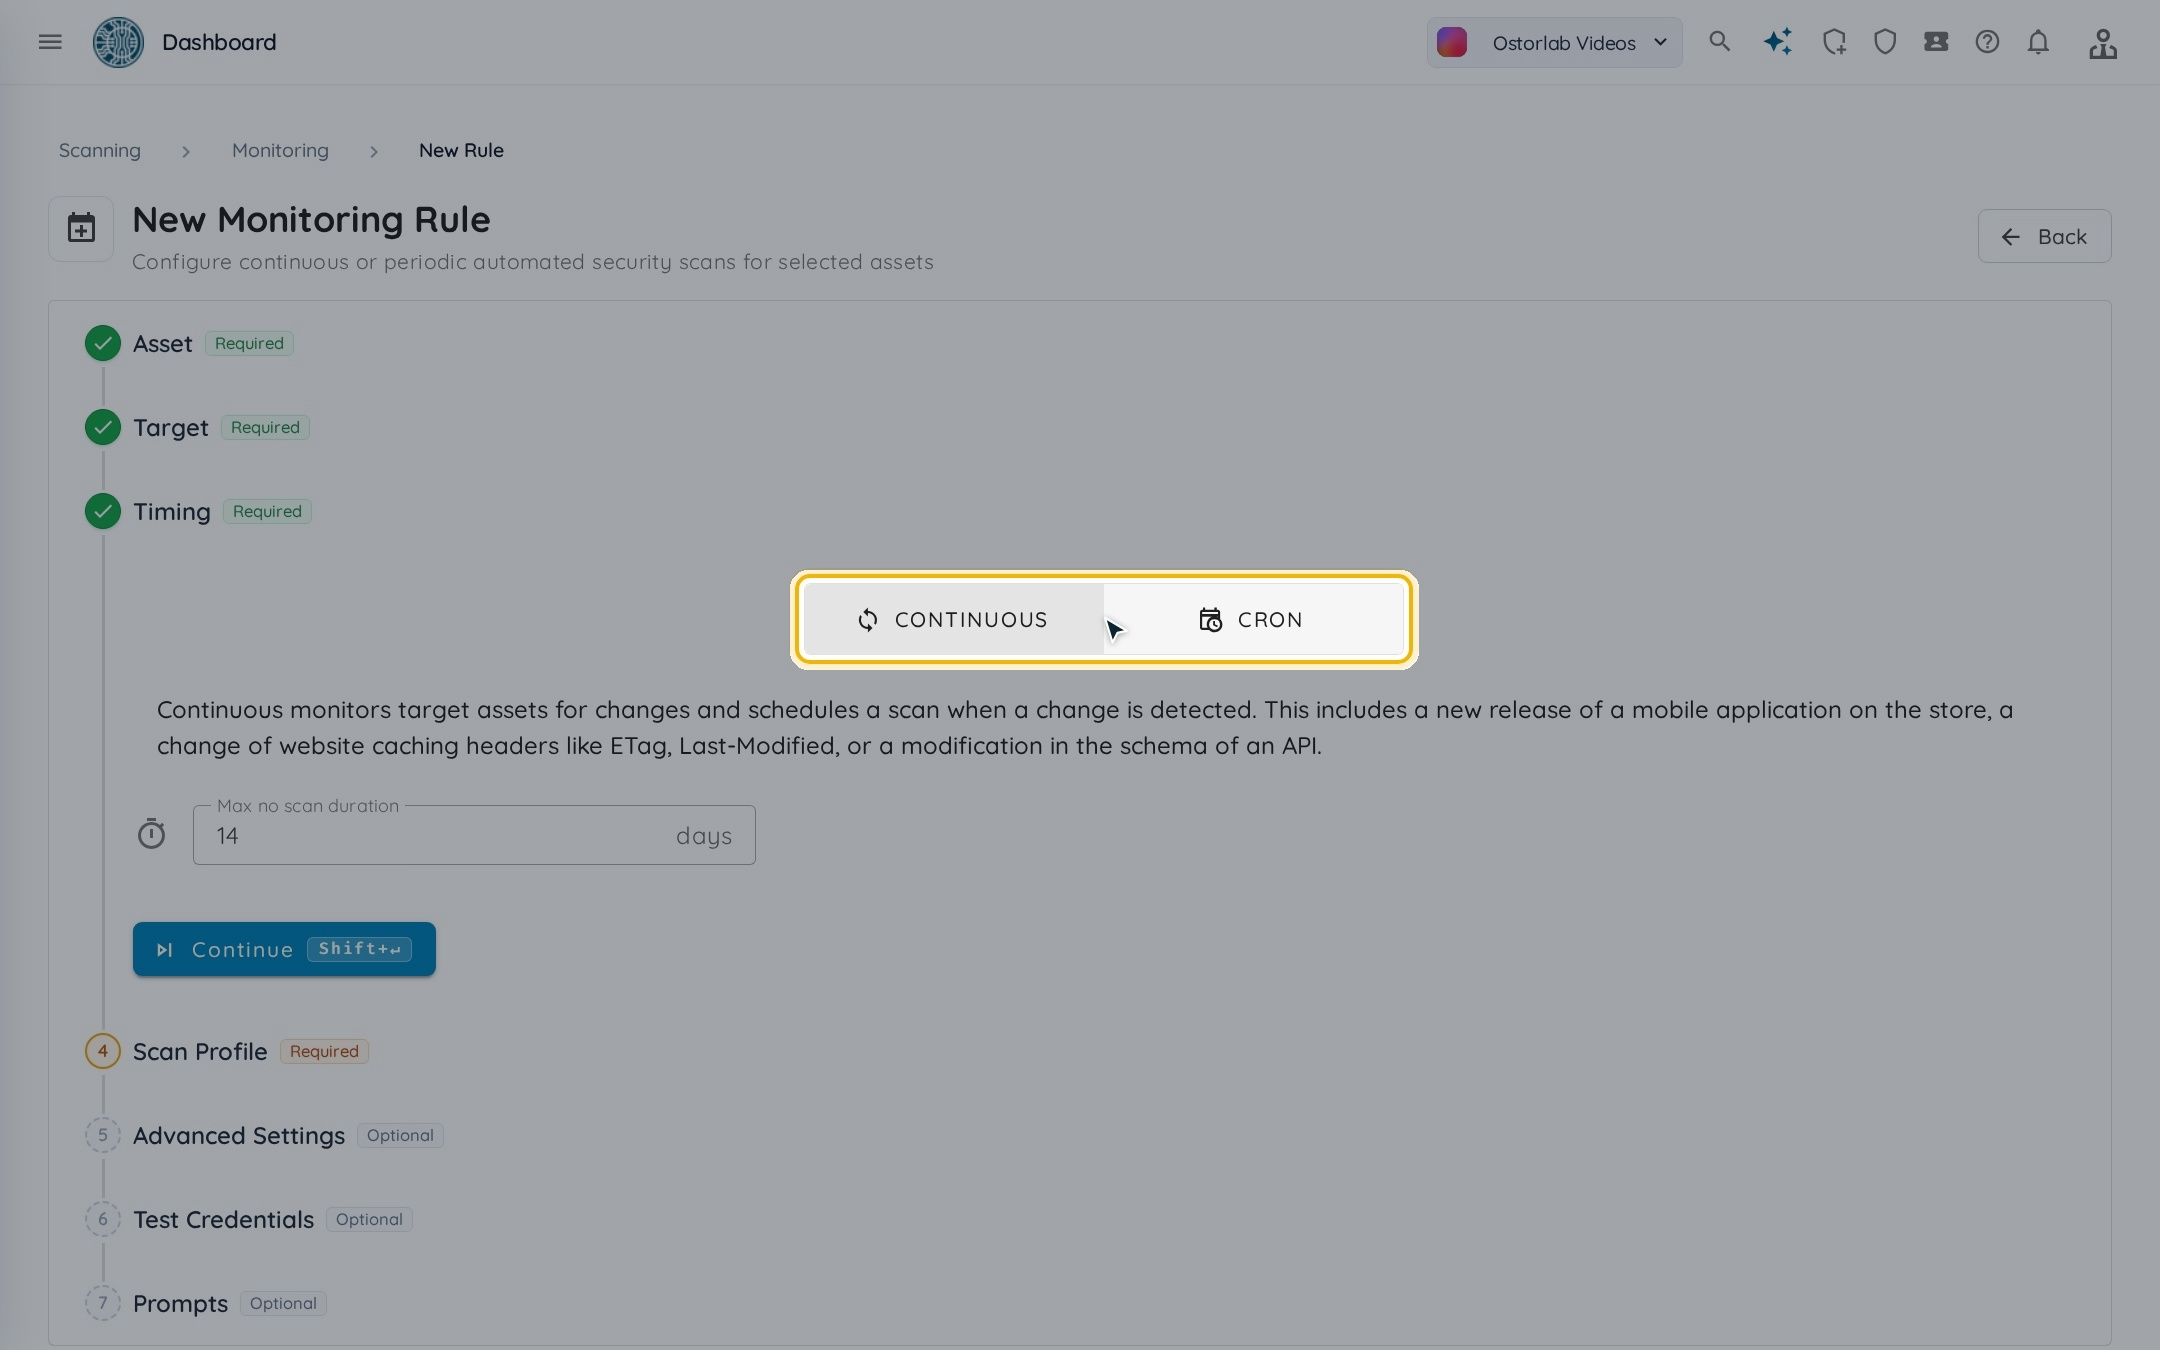
4. Set the timing
- Continuous: watches the assets and schedules a scan when one changes, like a new release of a mobile application on the store, a change of website caching headers like ETag or Last-Modified, or a change in the schema of an API. Max no scan duration starts a scan after that many days even if nothing changed.
- Cron: scans on a schedule, like once a week, once a month or the first Monday of each month.
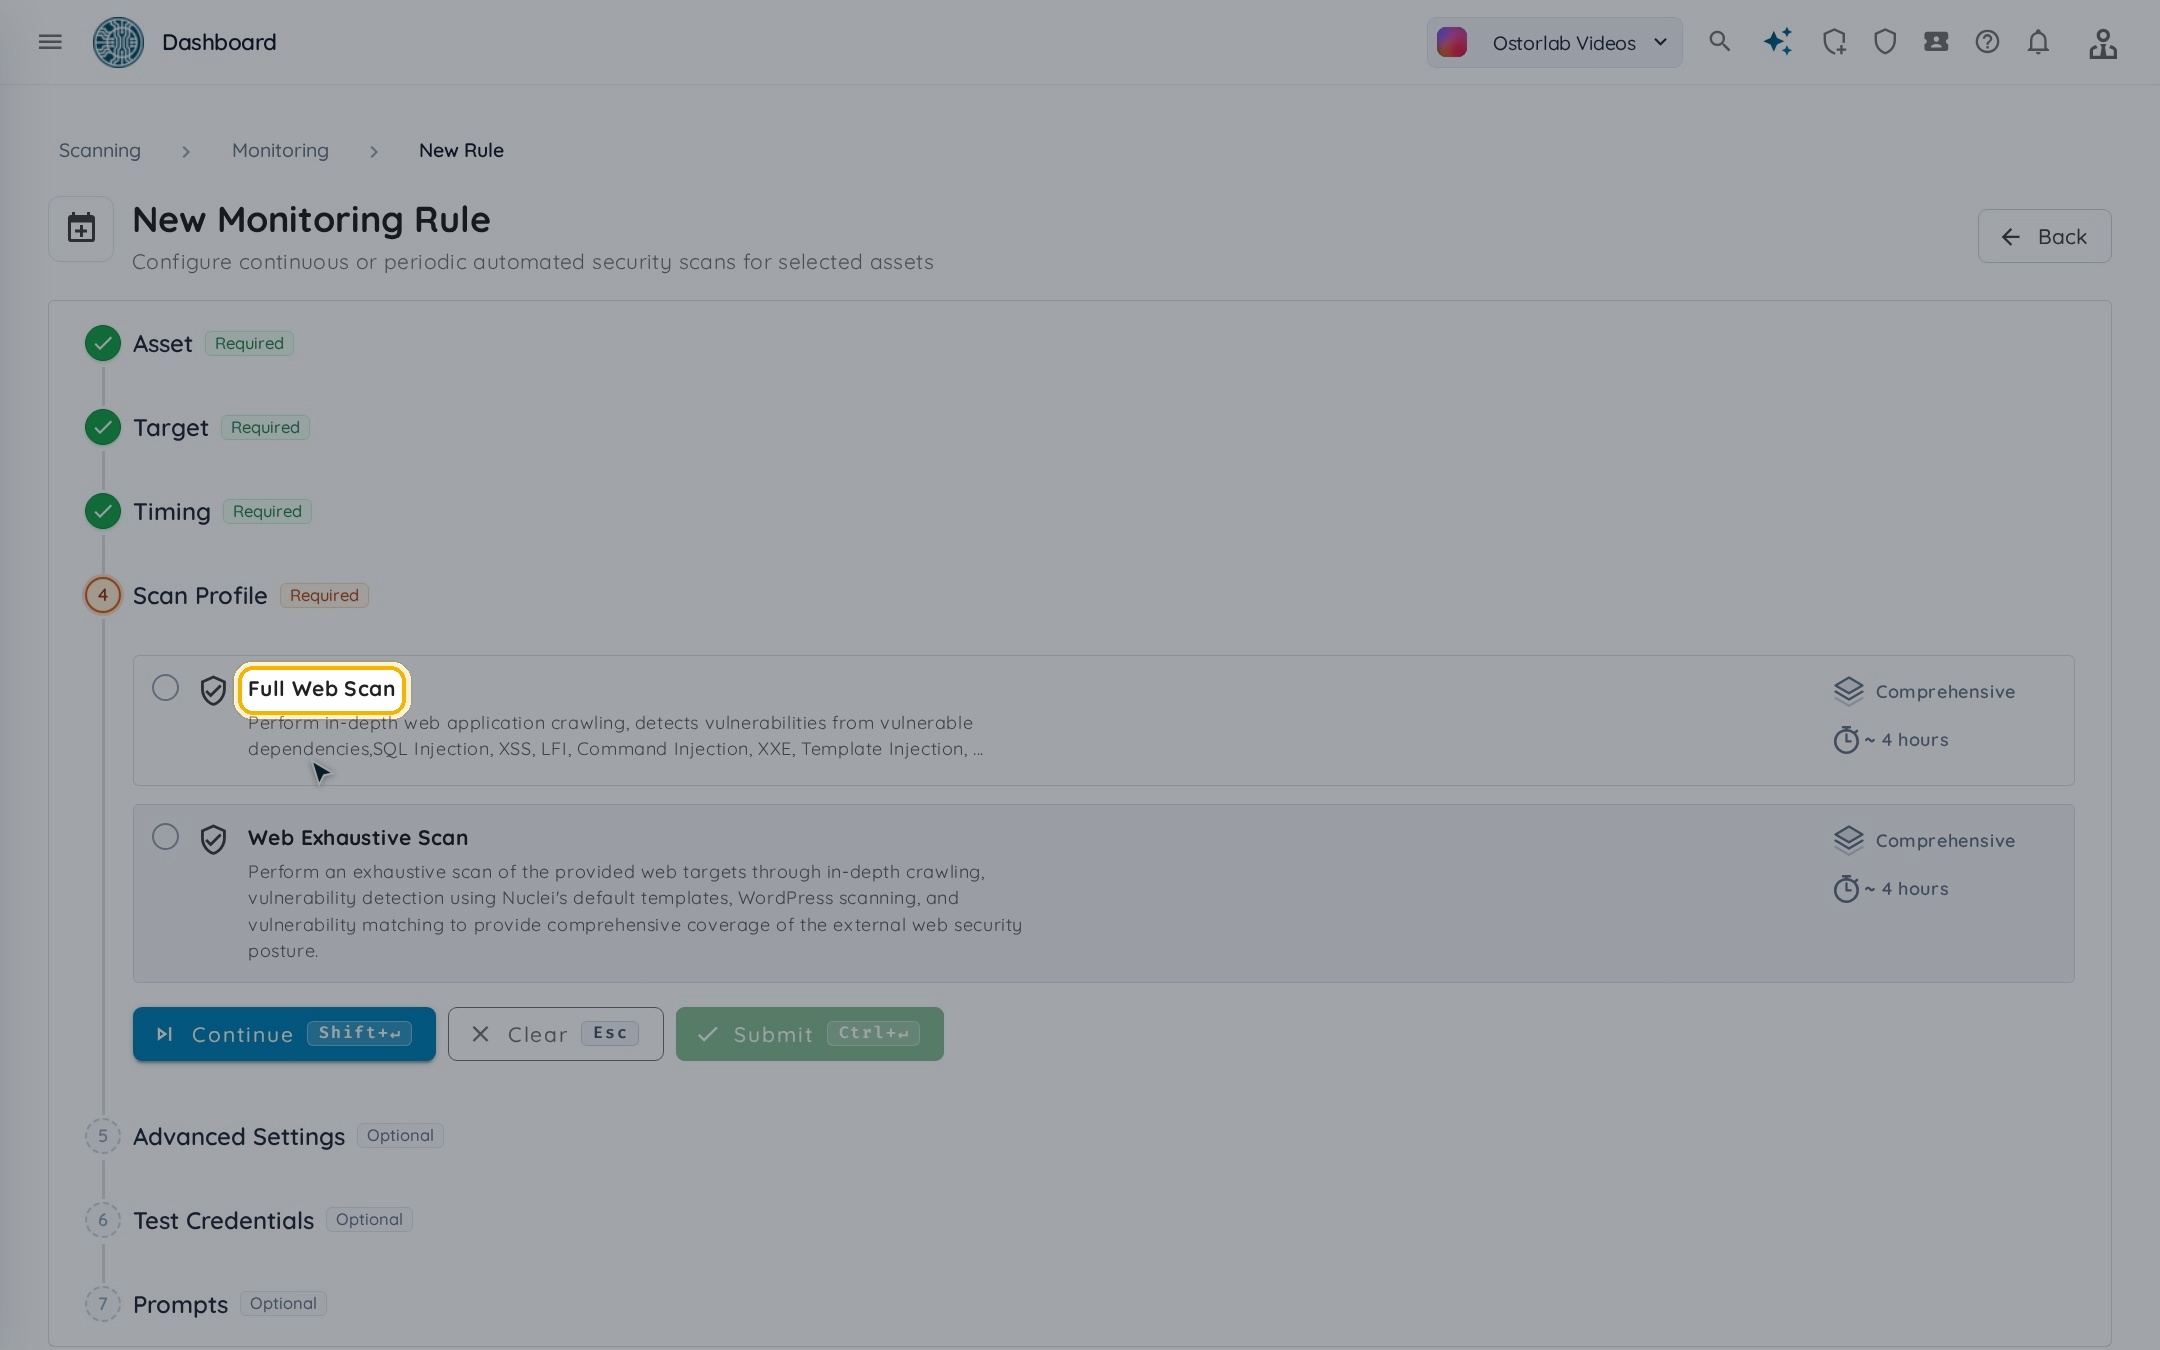
5. Choose the scan profile
The profiles depend on the asset type and on your plan.
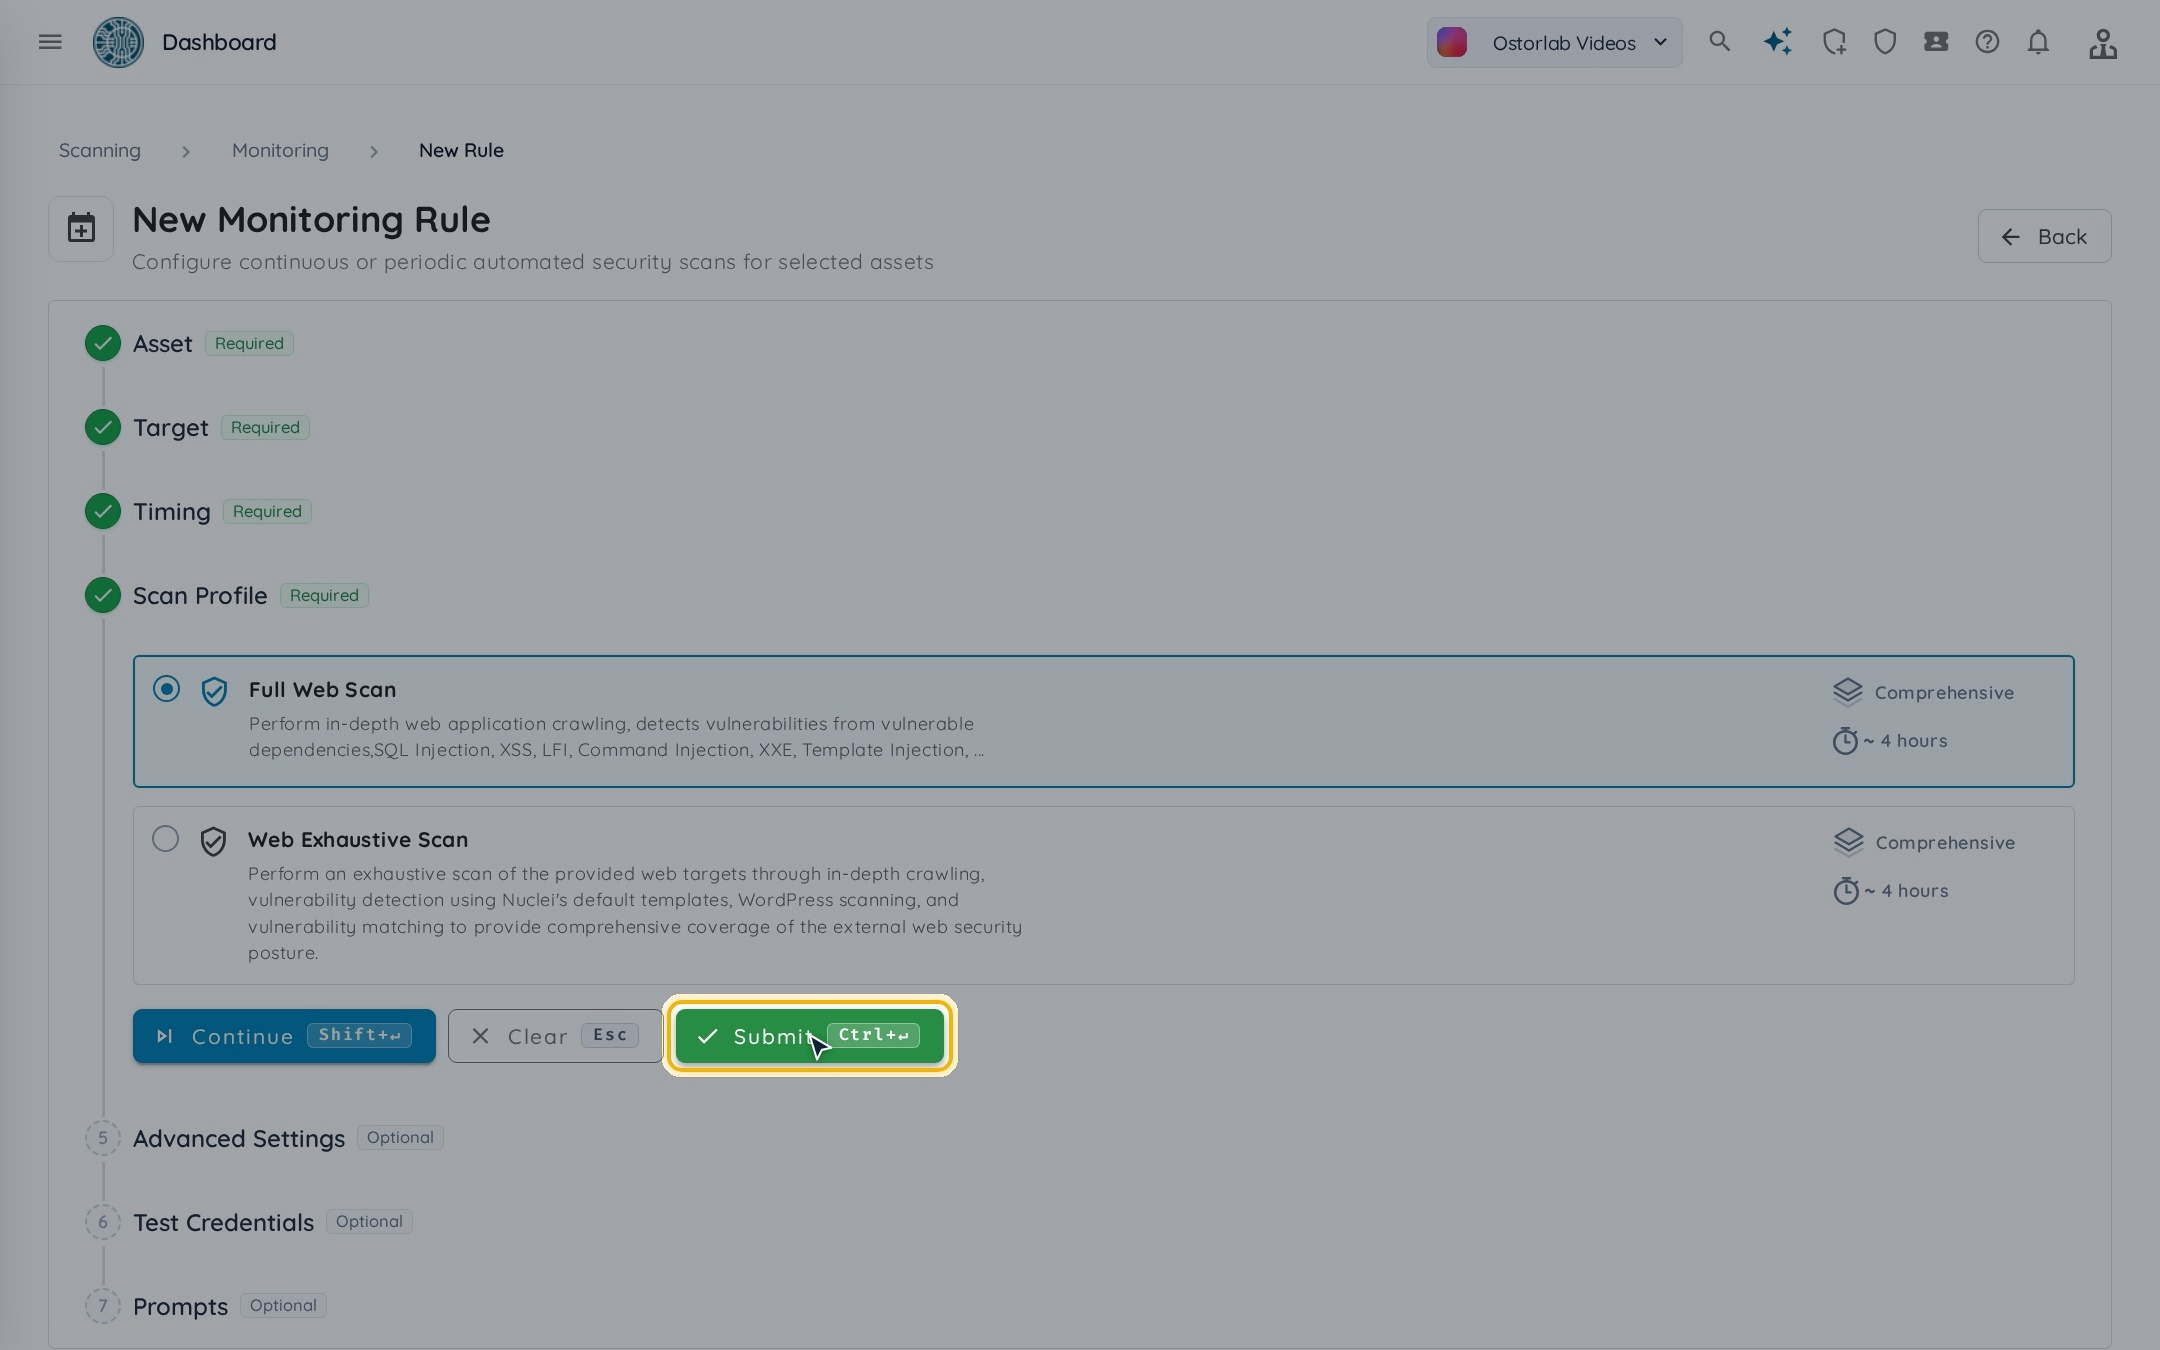
6. Click Submit
Advanced Settings, Test Credentials and Prompts are optional. Click Submit to create the rule.