Attack Surface
Discover Assets
Discovering Assets
Asset discovery is a continuously running process to find new assets as they appear, and in this guide we will walk you through this process.
Go to your organisation's dashboard.
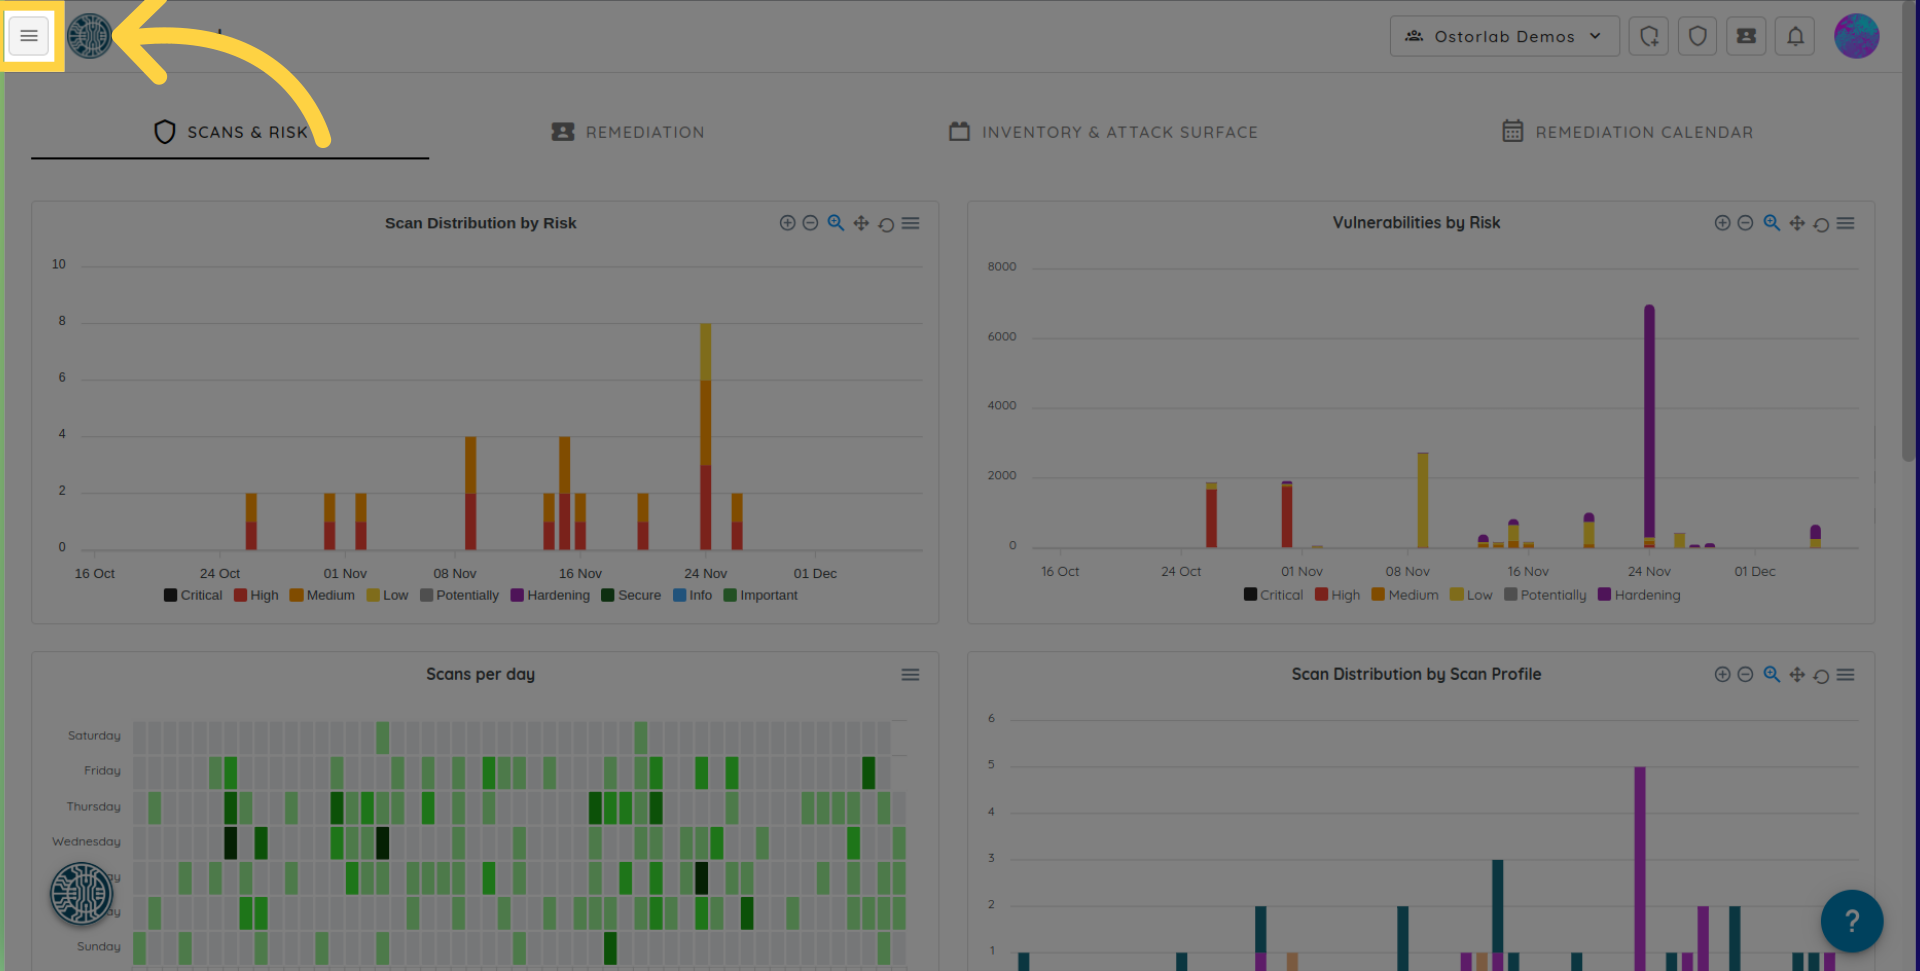
Navigate to the Attack Surface page.
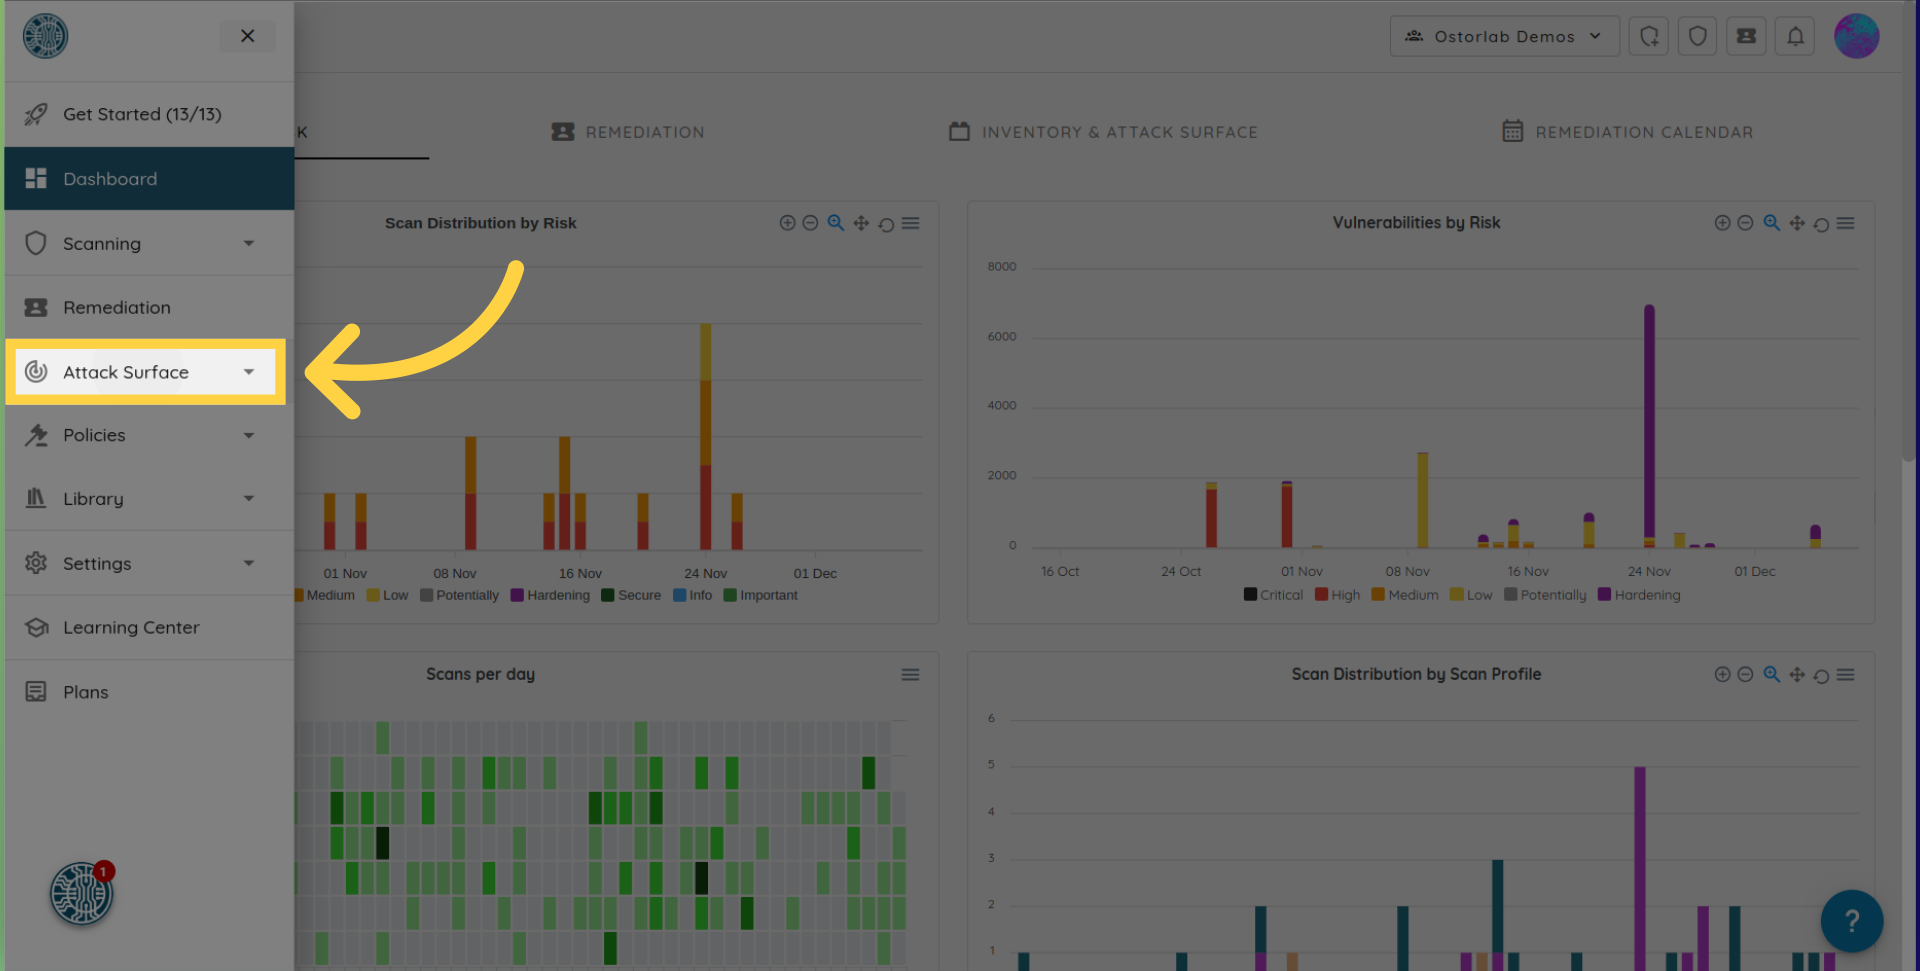
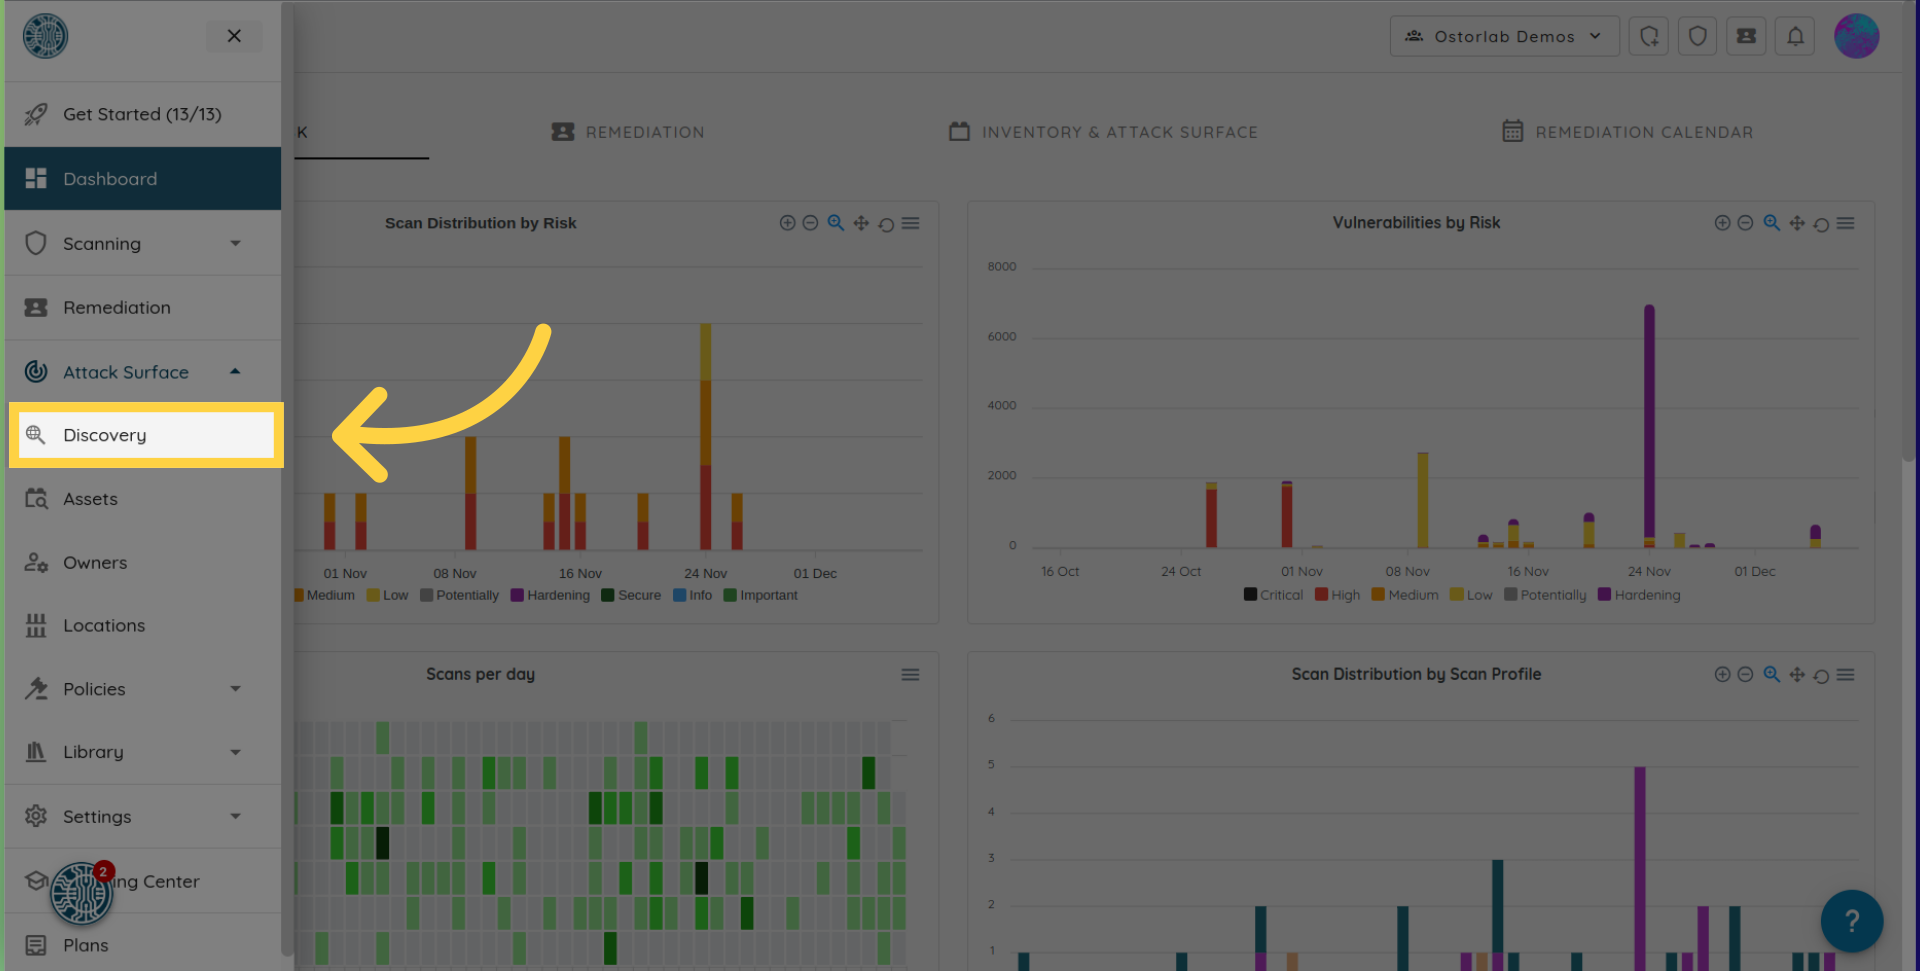
Then select the "Discovery" option from the menu.
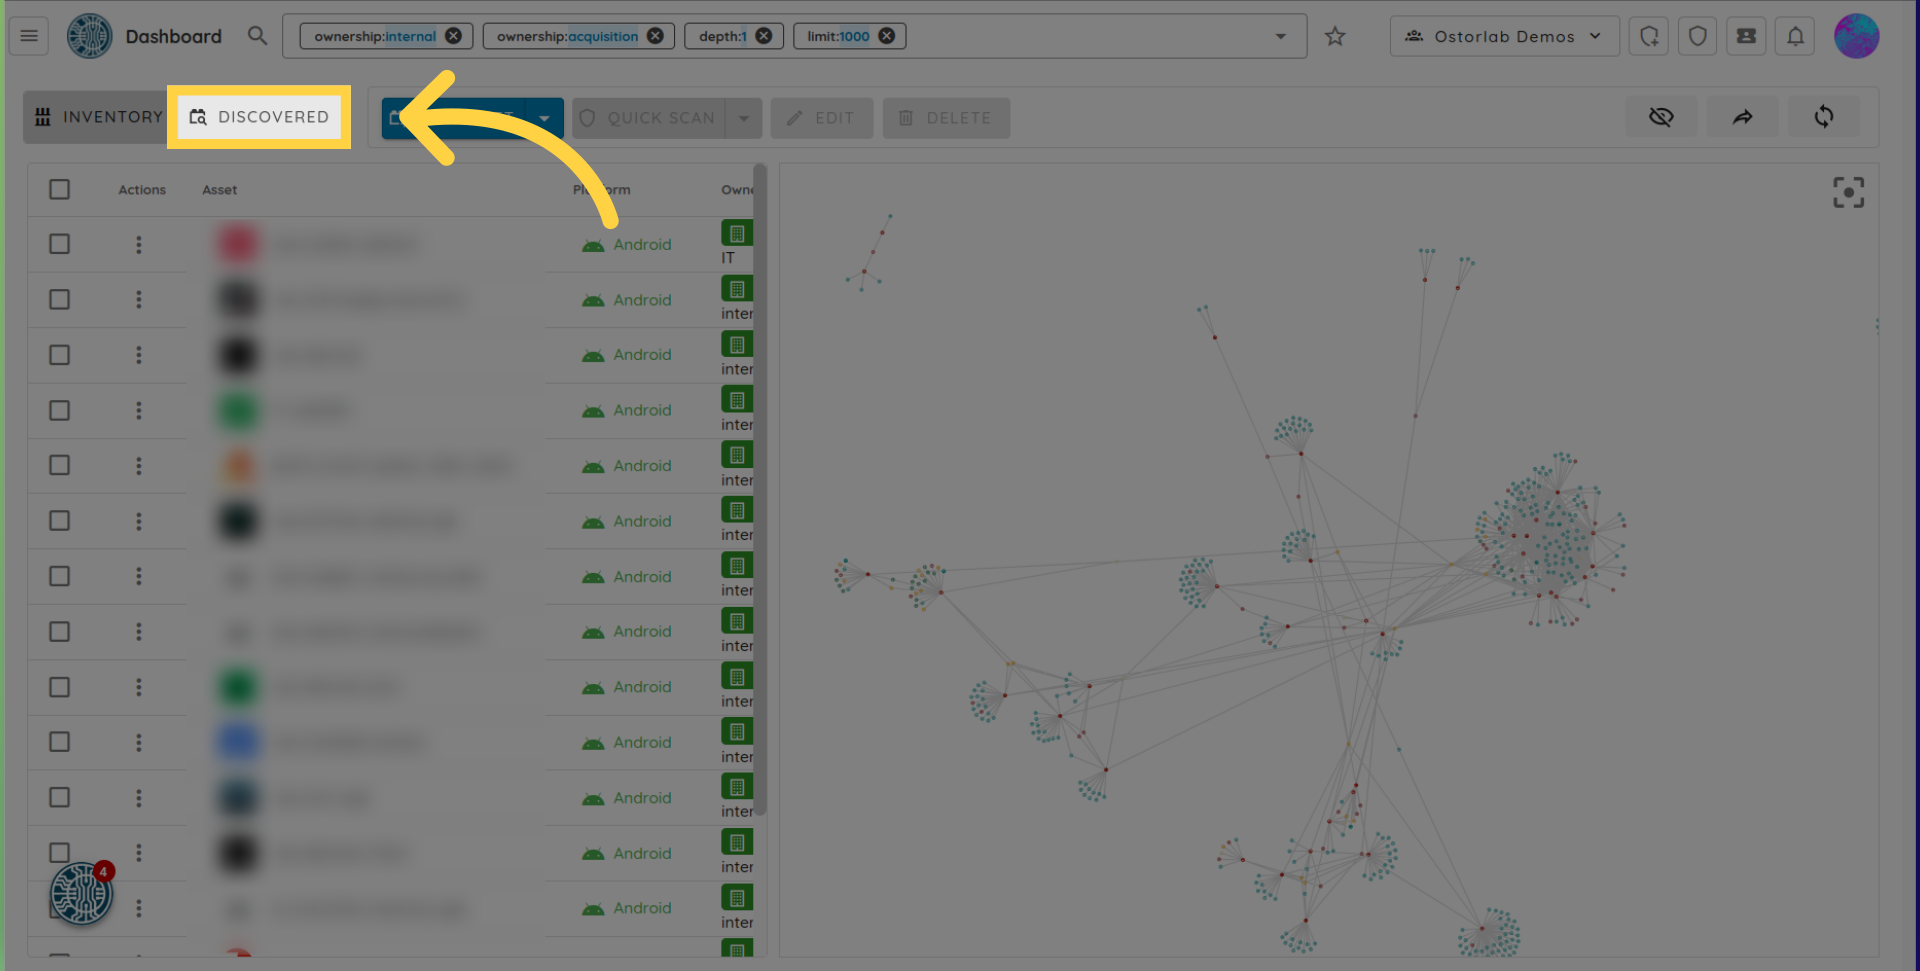
To list potential assets, change
the view mode to Discovered in the top-left corner. The assets table will show the
potential assets ordered by confidence, which can be High, Moderate or Low. The confidence has a score that
computes the likelihood an asset belongs to the same org as the confirmed ones.
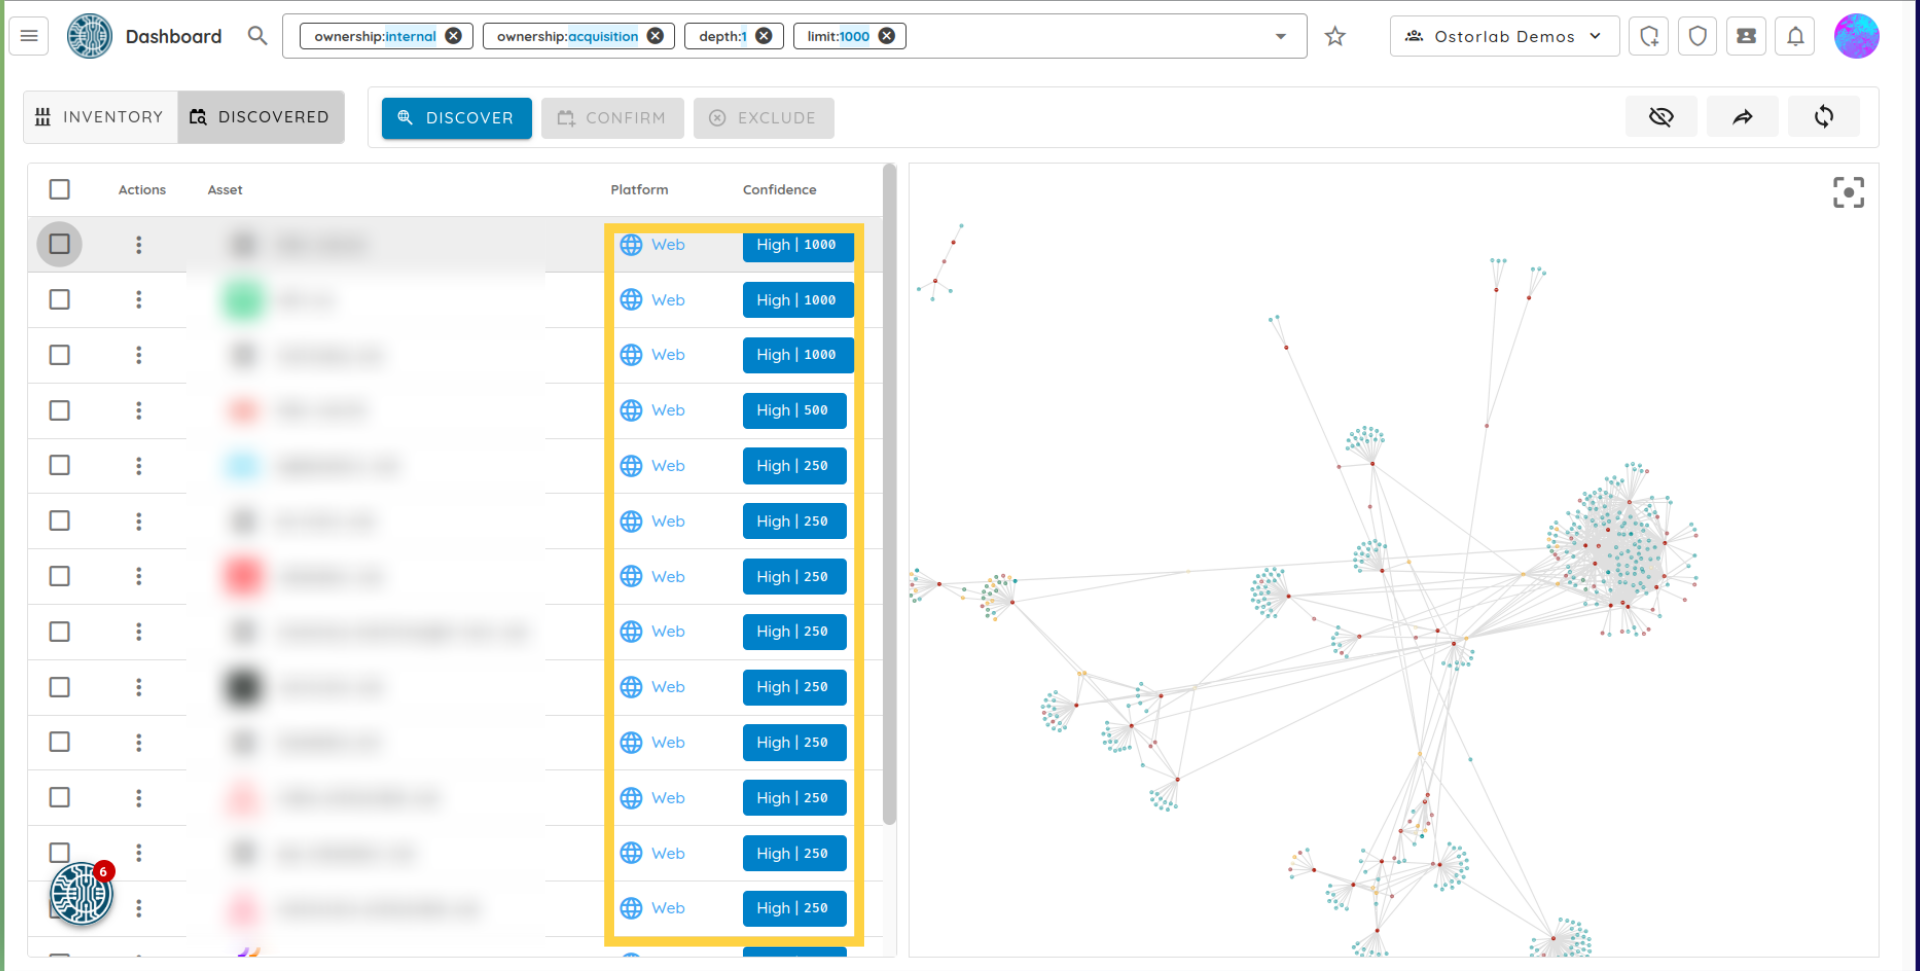
The more assets are confirmed, the better the platform learns how an organization is structured and can make better recommendations.
Discovered assets can either be confirmed by clicking the assign owner button or
rejected by disqualifying any of their connections. An example is a domain name with a CNAME that points to a hosting service.
The hosting service should be excluded to disqualify assets pointing to the same hosting provider. This can include 3rd party services
like a DNS service, a CDN, or a SaaS provider.
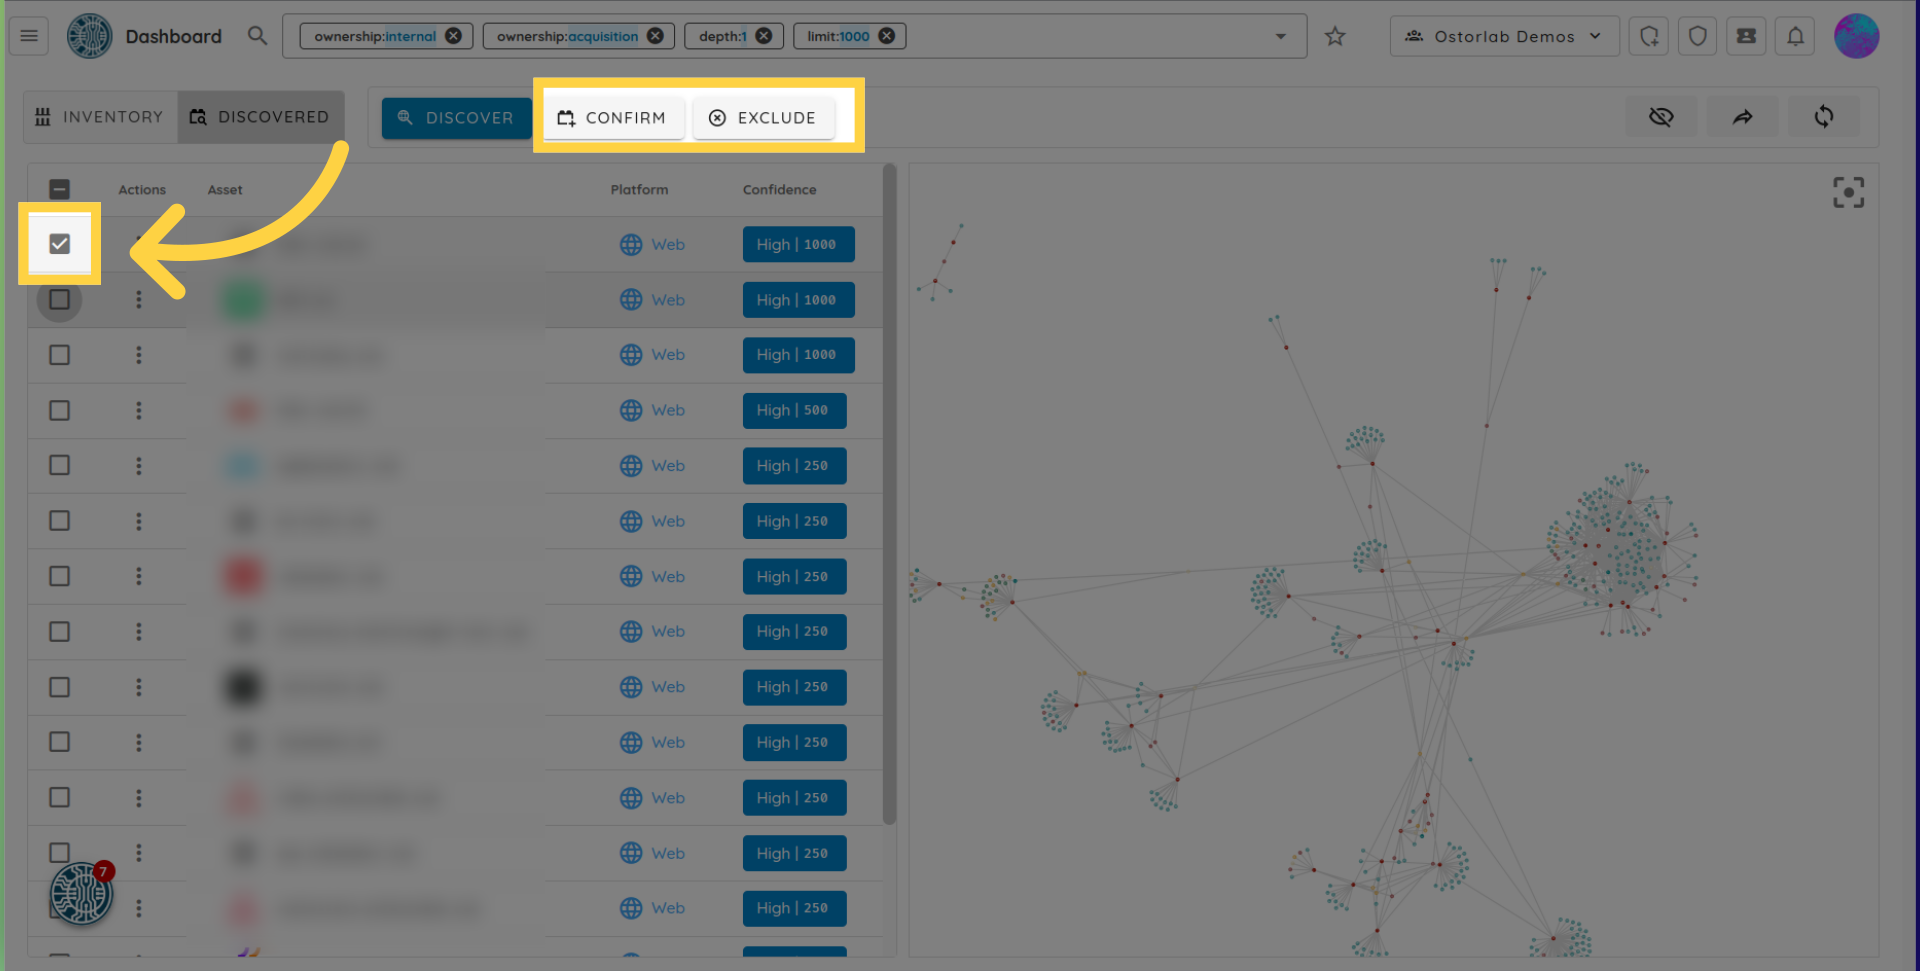
The discovered assets have several types, like domain, subdomain, IP, and Mobile App, organization, address, geolocation, TLD, person, email, ASN, etc.
These can also be confirmed as belonging to the organization to fine-tune the asset discovery algorithm. For instance, if an email is confirmed as belonging to an organization, all Whois records pointing to the email address will be qualified as potential nodes.