Monitoring
A monitoring rule re-scans your selected assets when they change or on a schedule, so you can find new vulnerabilities without repeating scans manually.
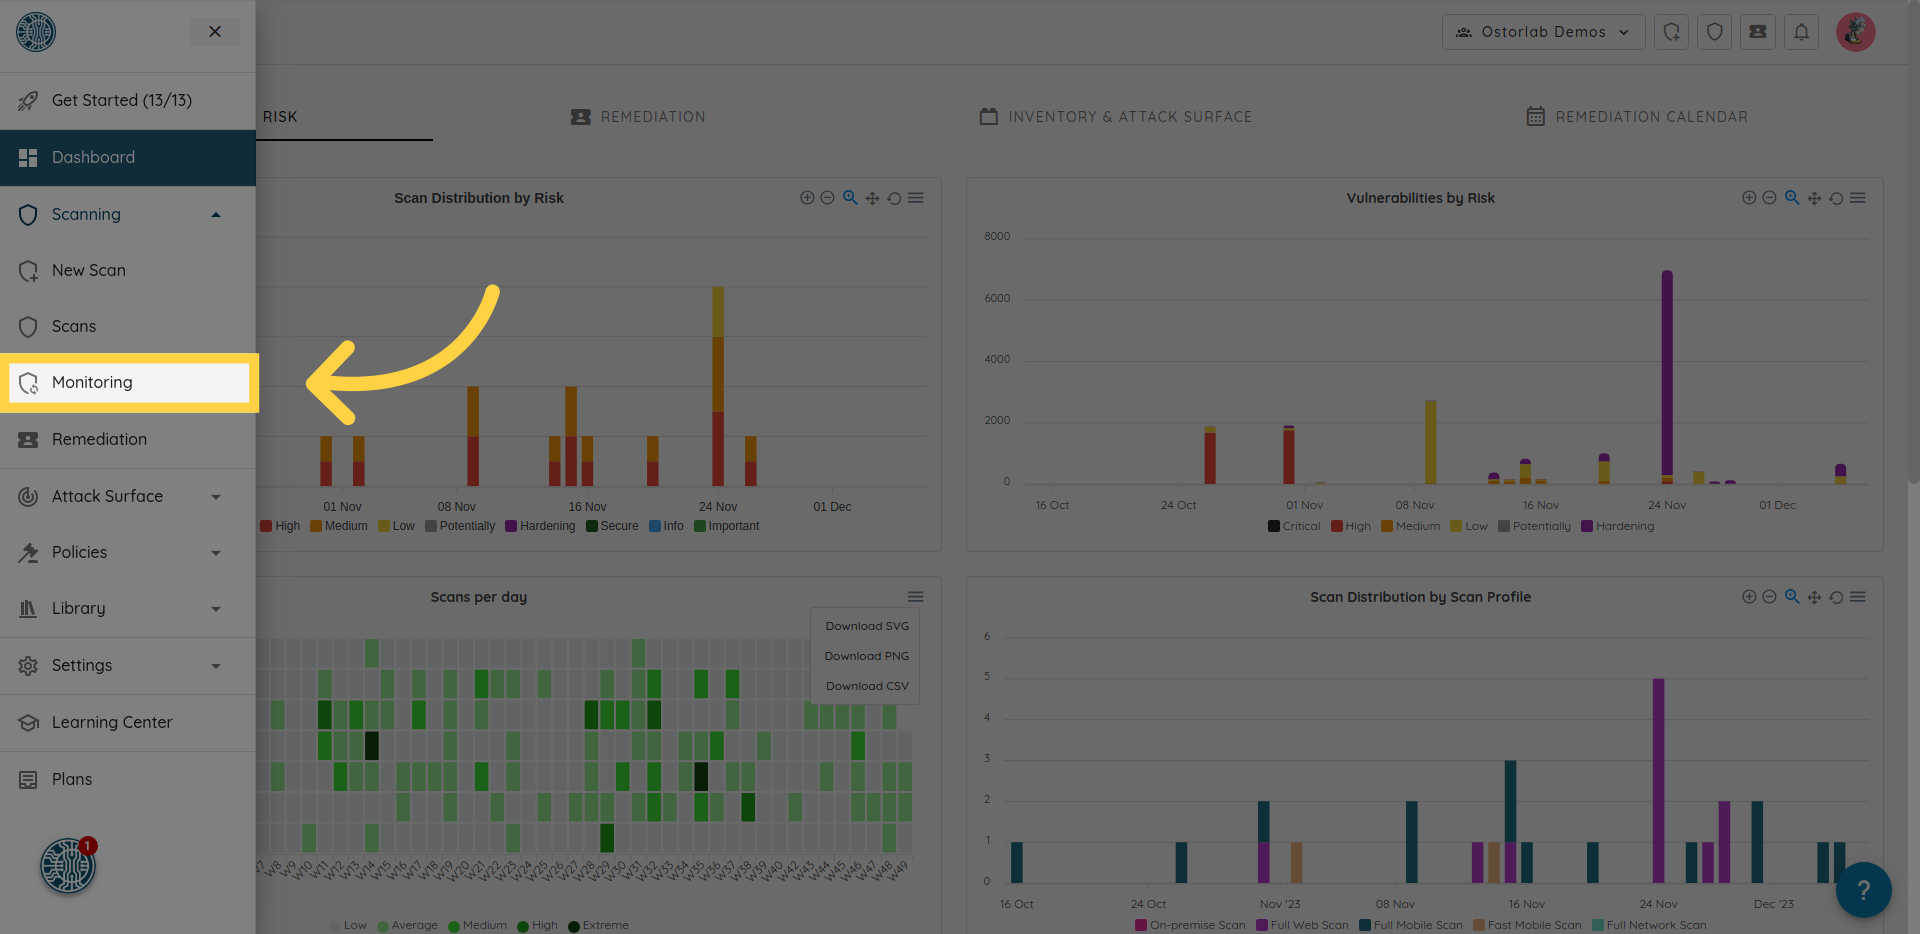
To manage rules, open the menu at the top left and choose Scanning > Monitoring.
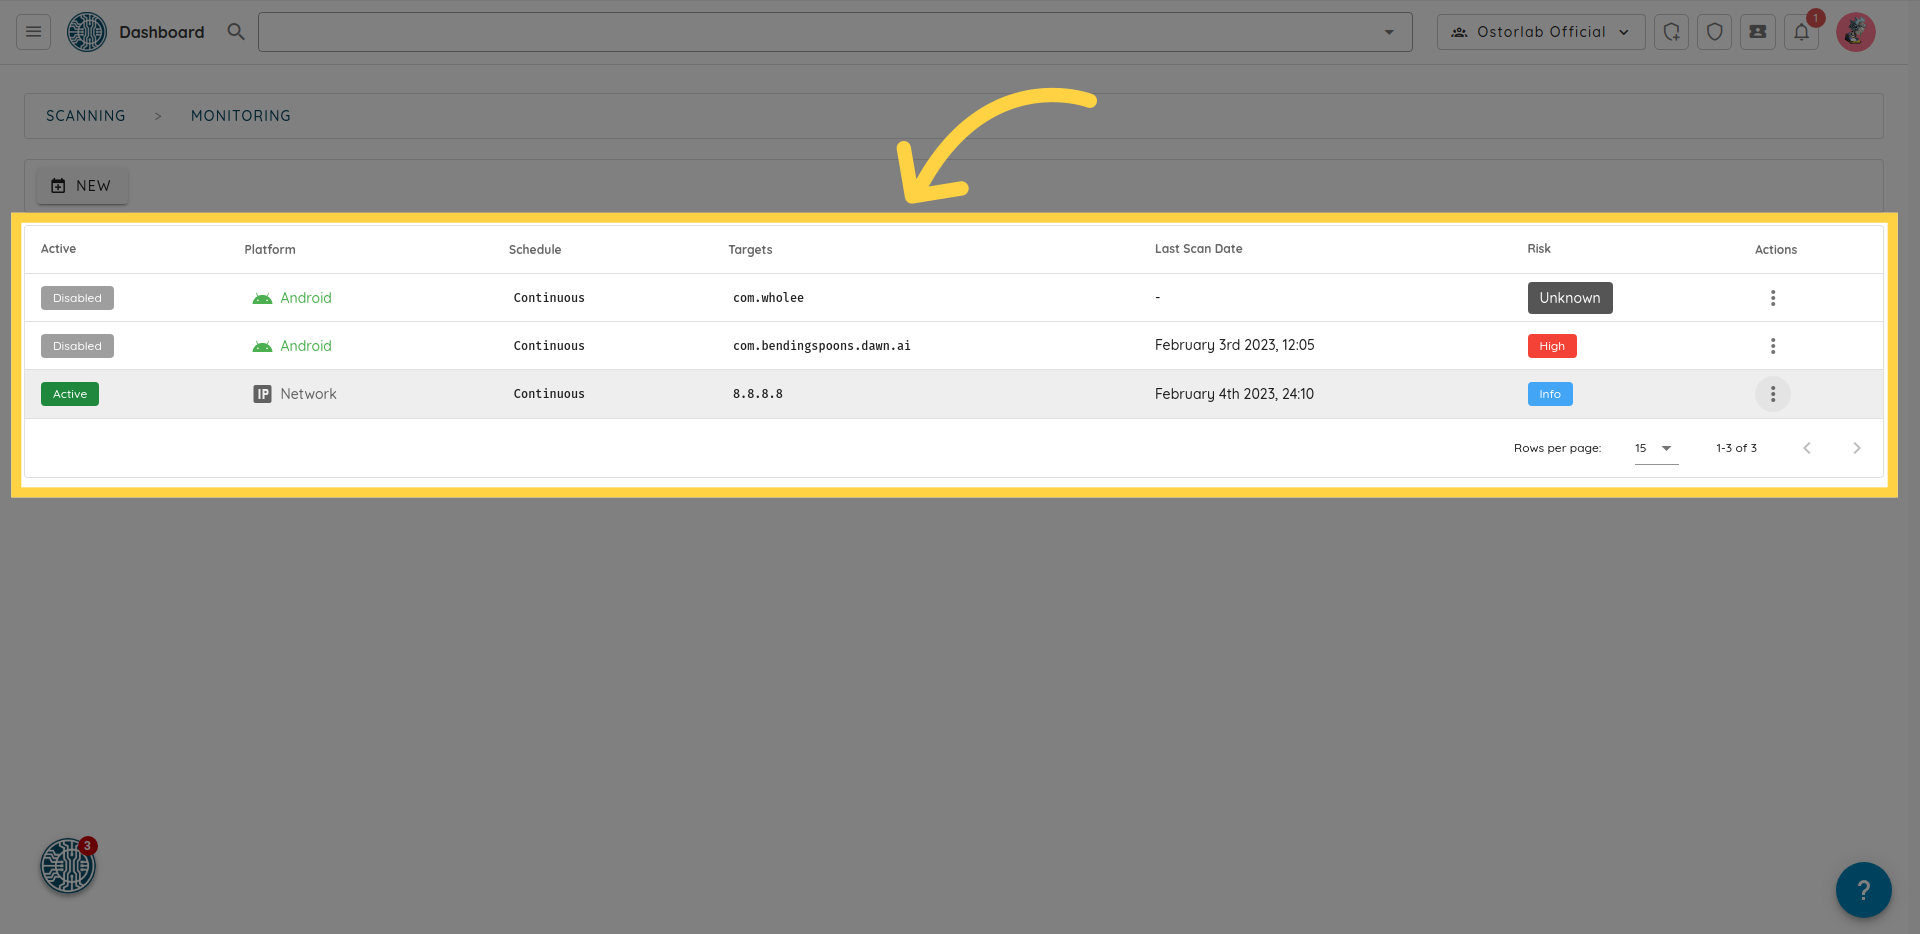
| Column | Meaning |
|---|---|
| Active | Whether the rule is active or disabled. |
| Platform | The monitored store or platform. |
| Scan Profile | The scan profile used for each run. |
| Schedule | Continuous monitoring or the cron schedule, evaluated in UTC. |
| Targets | The assets covered by the rule. |
| Last Execution | The outcome of the most recent execution. |
| Risk | The risk rating of the last scan. |
To create a rule, see Create Monitoring Rule.
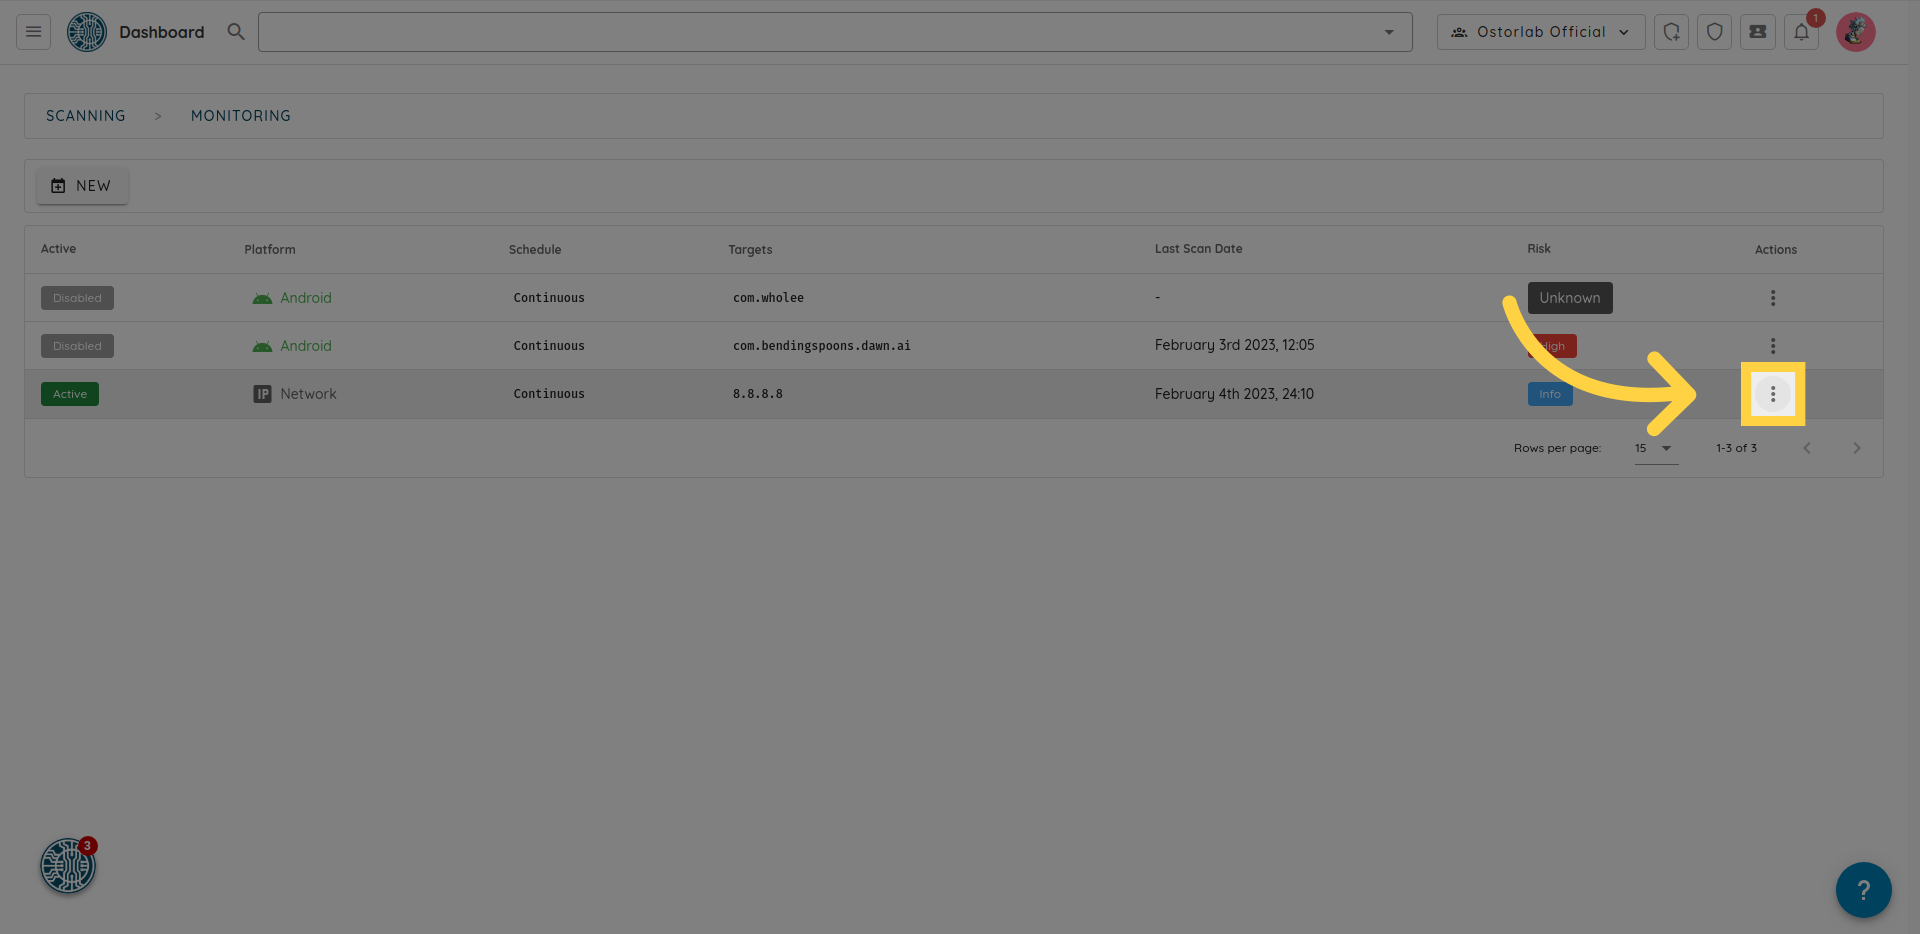
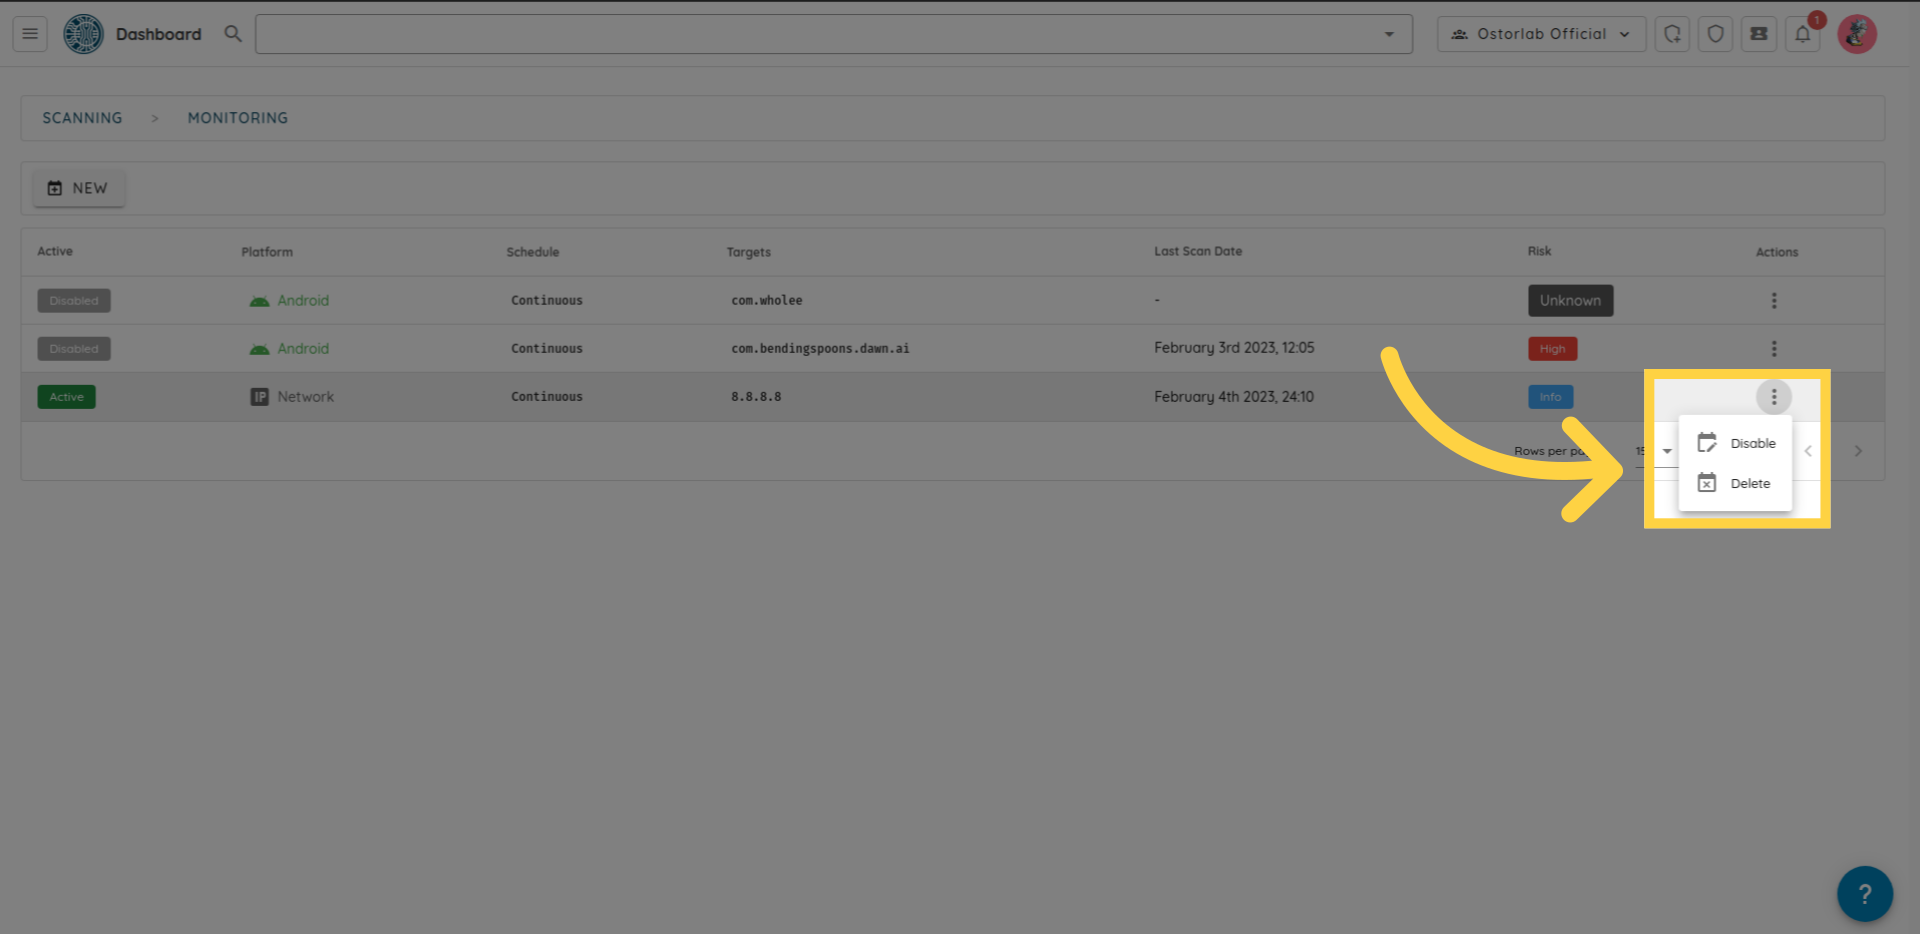
To edit, disable or delete a rule, or to see its execution history, click the three dots on the right.